As an industry leader in cybersecurity and compliance, Rhymetec is proud to partner with Vanta to deliver a complete solution for modern businesses. As Vanta's first MSP partner, we combine Vanta's compliance automation with Rhymetec's hands-on security and compliance expertise to accelerate readiness, strengthen your security posture, and reduce the time and effort required to meet regulatory requirements.
The Rhymetec + Vanta advantage
Rhymetec leverages Vanta to turn compliance automation into a practical, managed security and compliance program. Over the last decade, we've helped more than 1,000 organizations around the world meet their security and compliance goals.
“What makes the Rhymetec and Vanta partnership so valuable is how well our capabilities complement each other.
Vanta gives organizations the automation and visibility to manage compliance more efficiently, while our team brings the expertise to put those capabilities into practice and keep the program moving forward.”
— John Hibbeler, Partnerships Manager, Rhymetec
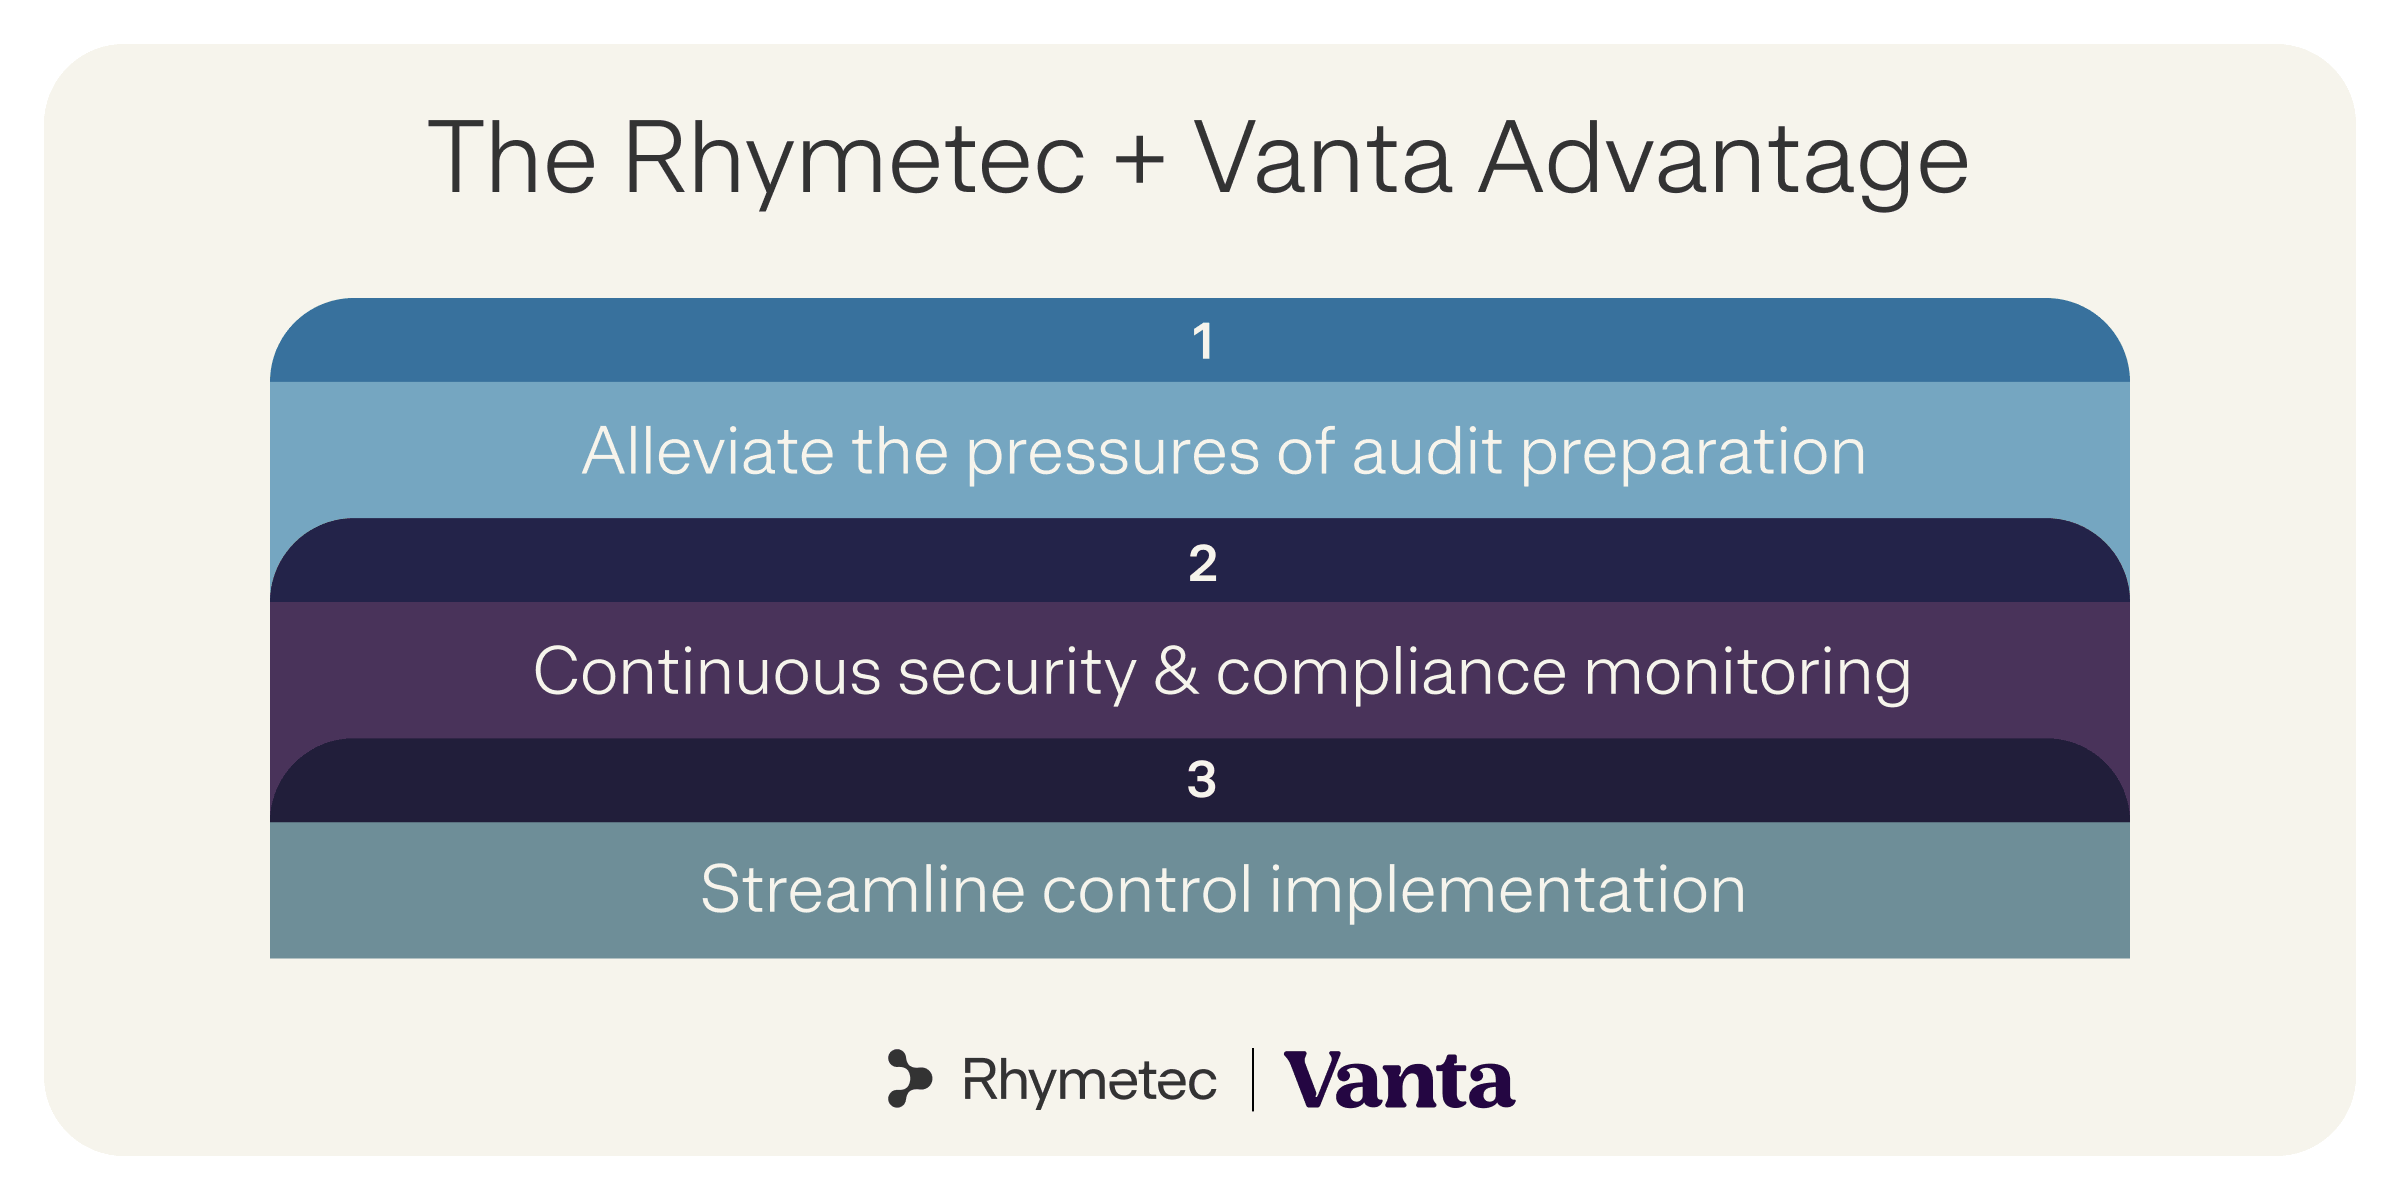
With our joint services, you can:
1. Reduce the burden of audit preparation
Vanta provides a centralized source of truth for compliance, helping organizations organize evidence, monitor controls, and track audit readiness. Rhymetec ensures the required documentation, evidence, and manual activities are addressed and manages the audit preparation process using Vanta as a central platform.
2. Maintain continuous security and compliance
Vanta's automation and continuous monitoring capabilities help organizations maintain visibility into their compliance posture between audits. Rhymetec's vCISO and compliance services provide the ongoing security guidance, remediation support, and questionnaire assistance needed to maintain and mature your program as your business evolves.
3. Streamline control implementation with Vanta
Rhymetec implements the controls required by your selected compliance framework and aligns them to your organization's actual environment and operations. Vanta supports this process through system integrations, automated evidence collection, continuous monitoring, and visibility into areas that require attention.
Together, Vanta and Rhymetec provide an integrated approach to compliance that combines automation with hands-on expertise, reducing the administrative burden on internal teams while keeping your program moving forward.
Our team at Rhymetec leverages Vanta to transform compliance from a complex challenge into a strategic advantage for your business. Over the last decade, we've helped over 1,000 companies around the world meet their security and compliance goals.
With our joint services, you can:
Our Vanta compliance services
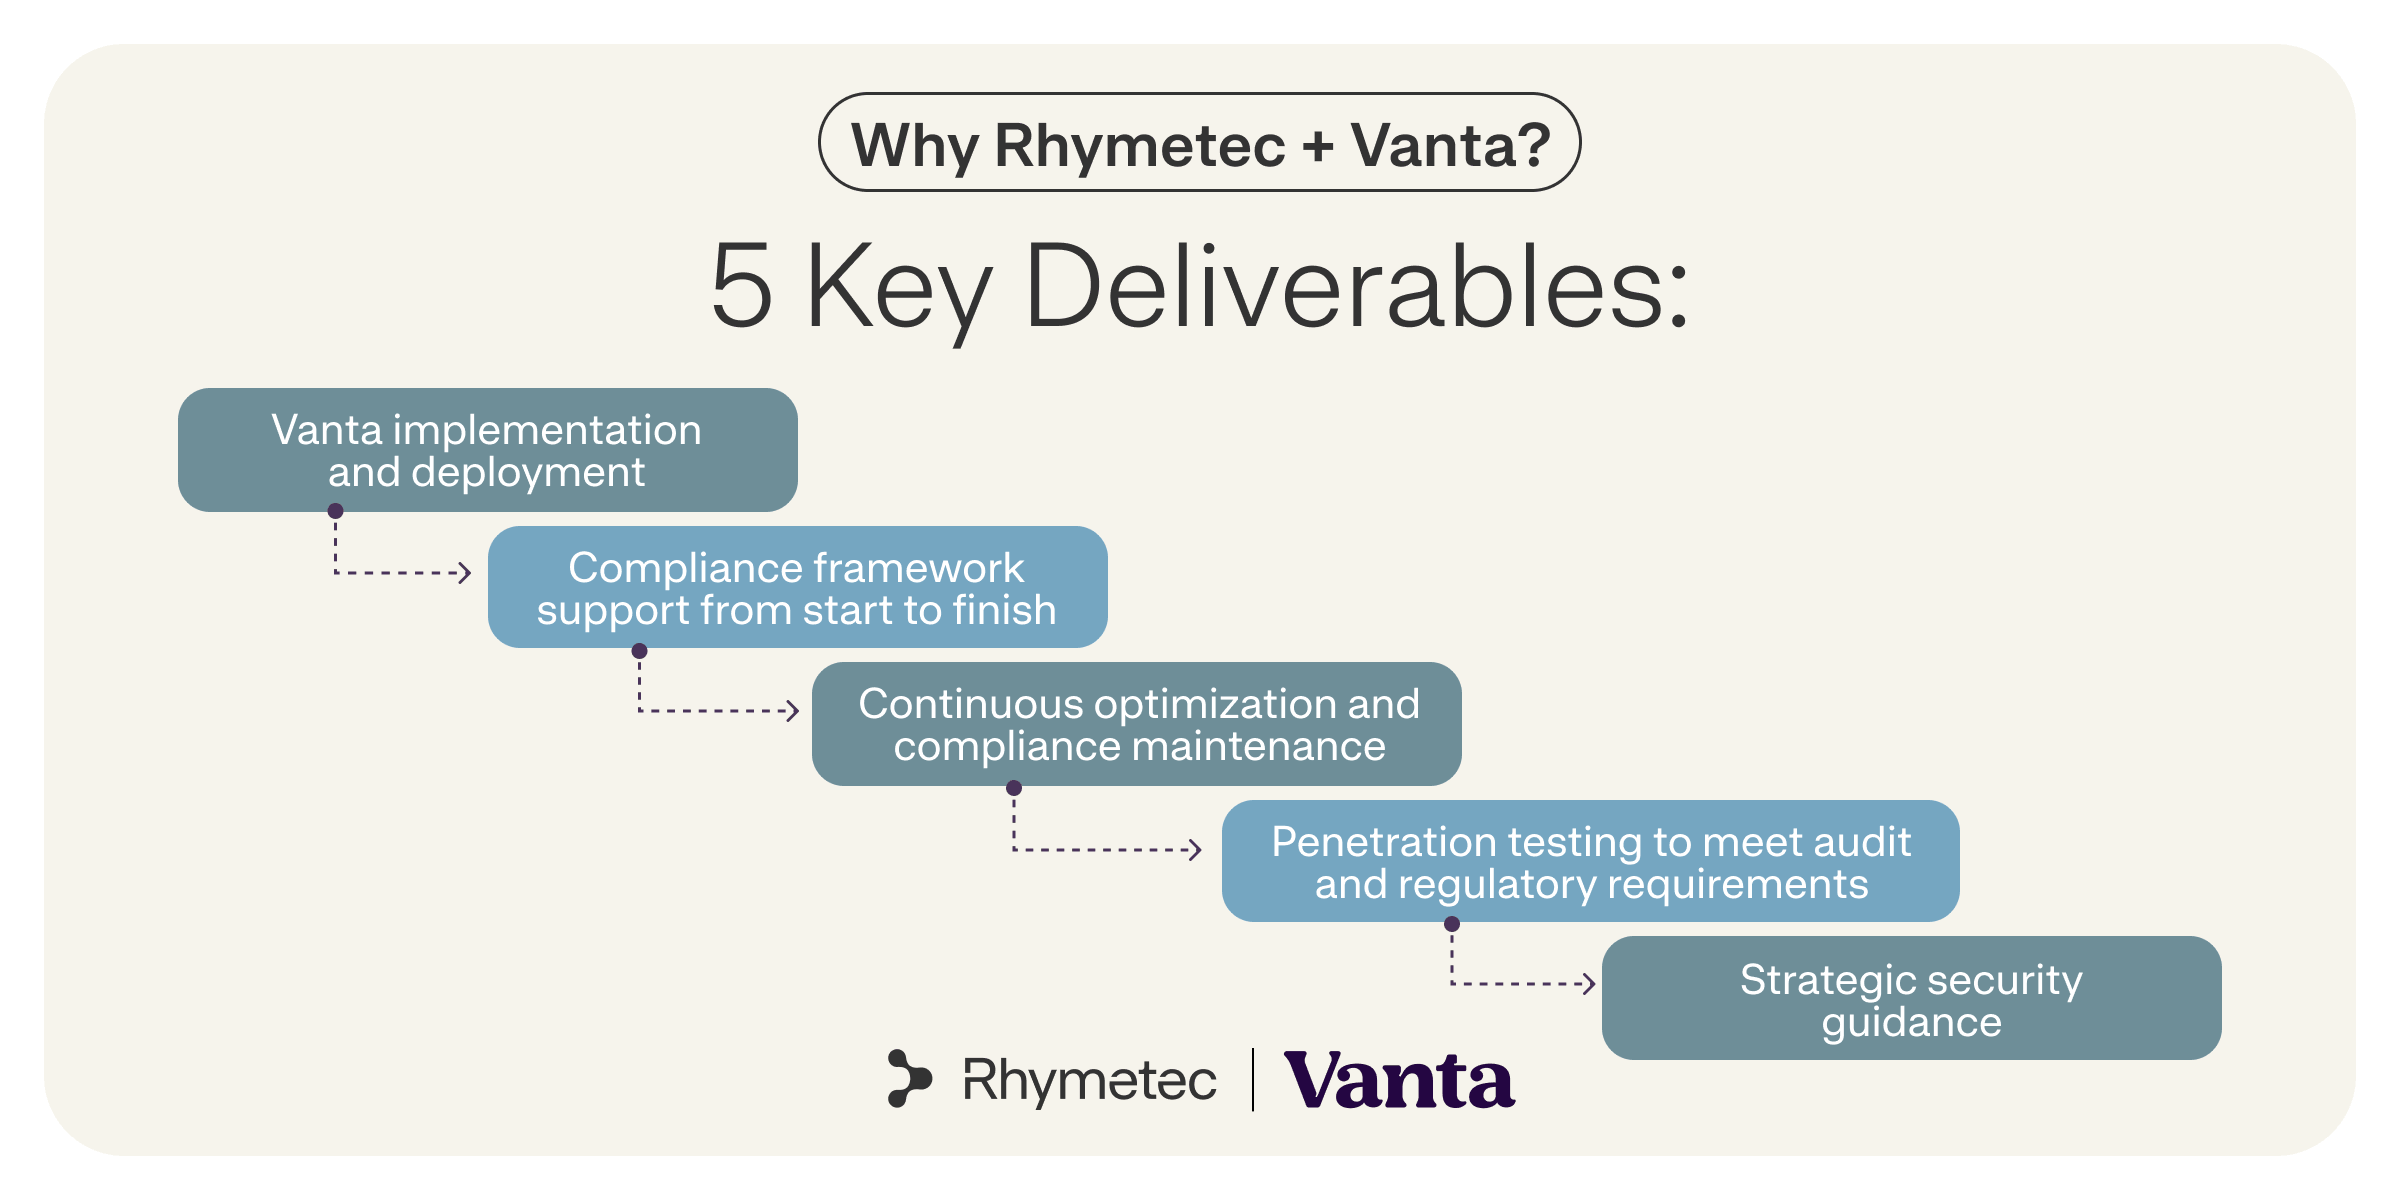
Vanta implementation and deployment
Vanta automates more than 90% of compliance work through 300+ integrations, continuous control monitoring, and automated evidence collection.
Rhymetec configures and deploys Vanta on your behalf, integrating the platform with your infrastructure to maximize its automation capabilities. We connect relevant systems, establish automated workflows, and configure policies and controls around your organization and selected compliance framework.
With Rhymetec managing Vanta deployment, your team can avoid the complexity of configuring integrations and building the platform from scratch. From the initial setup forward, we establish a reliable compliance foundation and reduce the burden on your internal resources.
Compliance framework support from start to finish
Vanta provides pre-built content and controls for 20+ major frameworks and standards, including SOC 2, ISO 27001, HIPAA, and GDPR. The platform helps automate scoping, evidence collection, monitoring, and document management while providing a foundation for policy and control management.
Rhymetec aligns these automated capabilities with your business needs and selected framework, handling the work that requires human judgment and implementation. This can include internal audits, tabletop exercises, risk assessments, penetration testing, evidence preparation, policy development, and remediation.
Managing compliance without dedicated expertise can result in missed requirements, ineffective controls, or unnecessary work. By managing the full compliance process, Rhymetec helps reduce uncertainty, accelerate readiness, and ensure your program is appropriately aligned to auditor and regulatory expectations.
Continuous optimization and compliance maintenance
Vanta's continuous monitoring identifies failing controls, missing security measures, and other changes that may affect your compliance posture. Automated notifications and remediation workflows help surface issues and keep them moving toward resolution.
Rhymetec oversees these findings, interprets their impact, and performs or coordinates the manual remediation required to address them.
Ongoing compliance requires more than preparing for an annual audit. With Rhymetec managing continuous monitoring and remediation alongside Vanta's automation, your organization can maintain visibility into its security posture, reduce compliance drift, and address gaps before they become larger issues.
Penetration testing to meet audit and regulatory requirements
Many voluntary frameworks and regulatory requirements include expectations around penetration testing and security testing.
SOC 2, PCI DSS, ISO 27001, CMMC, and HIPAA include requirements related to testing security controls, networks, applications, or systems. Regulations such as GDPR and CCPA also emphasize appropriate technical and organizational security measures to identify and address vulnerabilities.
Rhymetec began as a penetration testing company in 2015. Today, our penetration testing services help organizations meet security and compliance requirements while strengthening their overall security posture. We provide detailed reports of findings and practical remediation recommendations, helping organizations address vulnerabilities before an assessment or audit.
We offer a range of penetration testing services to support different security and compliance requirements, including mobile application and web application penetration testing.
Strategic security guidance
Vanta's capabilities streamline core areas of security and compliance, including risk management, access reviews, vendor security assessments, and security questionnaires. The platform accelerates workflows and provides visibility into the state of your compliance program.
Rhymetec's team provides the expertise required to interpret those findings, implement security best practices, and align controls to your organization's unique risk profile and risk appetite.
Effective security and compliance programs must reflect how an organization actually operates. Rhymetec combines Vanta's automation and integrations with hands-on security expertise to build programs that address regulatory requirements while supporting operational efficiency and long-term business growth.
Why Rhymetec?
Transparency
We believe clients deserve clarity around what they're getting, how we work, and the results they can expect. From our methodologies and testing scope to the technologies we use, we provide visibility throughout the engagement.
Autonomous
As a self-funded company, Rhymetec has the independence to make client-focused decisions quickly and adapt our services to meet each organization's needs. Our independence allows us to focus on what matters most: delivering meaningful security and compliance outcomes for our clients.
Team credentials
Our team holds a broad range of industry-recognized certifications, including Burp Suite Certified Practitioner, CISSP, EC-Council CHFI and CPENT, Offensive Security certifications including OSE3, OSED, OSEP, OSWA, OSWE, and OSCP, CompTIA Security+, PECB Internal Auditor certifications, and more.
Market maturity
Founded in 2015, Rhymetec brings more than a decade of specialized cybersecurity and compliance experience to every engagement. Our team understands the practical challenges organizations face when building security programs, preparing for audits, and meeting evolving compliance requirements.
Frameworks supported by Rhymetec's Vanta compliance services
Achieve compliance readiness with Vanta's automation and Rhymetec's hands-on security expertise. Together, we streamline control implementation and manage the work required across the compliance lifecycle.
Rhymetec supports a broad range of frameworks and standards, including the following:
SOC 2
Vanta automates control monitoring, policy management, and evidence collection for SOC 2, reducing the manual effort required to prepare for an audit. Because SOC 2 allows flexibility in how controls are designed and implemented, organizations still need to determine how requirements apply to their specific environment.
Rhymetec ensures automated controls are appropriately scoped, addresses gaps through manual activities such as risk assessments and penetration testing, and guides your team through audit readiness.
ISO 27001
Vanta helps accelerate ISO 27001 readiness through automation across areas such as risk management, asset and system inventory, evidence collection, and document management.
ISO 27001 also requires organizational processes and ongoing activities that extend beyond automation, including internal audits, risk treatment, and continual improvement. Rhymetec manages these components, develops and refines policies, and aligns your Information Security Management System (ISMS) with your organization's risks and operations.
GDPR
Vanta supports GDPR compliance through capabilities such as access reviews, vendor risk assessments, security monitoring, and evidence management.
GDPR also requires legal, privacy, and operational processes that cannot be addressed through automation alone. Rhymetec supports activities such as data mapping, Data Protection Impact Assessments, incident response planning, privacy policy development, and data processing agreements to help align your program with applicable GDPR requirements.
HIPAA
Vanta supports HIPAA compliance by monitoring technical safeguards, access controls, security policies, and related evidence.
For administrative safeguards that require organizational processes and human oversight, Rhymetec helps implement and refine areas such as employee training, documented risk management procedures, and business associate agreements. Our team also provides guidance on regulatory expectations and how they apply to your environment.
PCI DSS
Vanta helps organizations monitor security controls and identify gaps related to PCI DSS requirements. Rhymetec addresses the technical and operational components that require hands-on expertise, including penetration testing, network segmentation, vulnerability management, and required security assessments.
By combining Vanta's automation with Rhymetec's technical security expertise, organizations can address PCI DSS requirements efficiently while establishing a sustainable approach to ongoing compliance.
CMMC
Vanta helps streamline CMMC compliance by automating areas such as security control monitoring, evidence collection, and access reviews.
CMMC requires organizations to implement and maintain a broad set of security practices across areas including access control, incident response, risk management, system and communications protection, and more. Rhymetec's team provides hands-on support to implement the necessary security measures, develop documentation such as System Security Plans, establish incident response processes, and address third-party risk management requirements.
FedRAMP 20x
FedRAMP 20x represents a significant modernization of the federal cloud security authorization process, introducing a more automation-ready approach built around measurable Key Security Indicators (KSIs). For cloud service providers pursuing federal business, understanding how these requirements apply to the organization's environment is an important first step toward readiness.
Vanta supports FedRAMP 20x with automated evidence collection, continuous testing, KSI-mapped controls, centralized workflows, and machine-readable outputs designed to support the FedRAMP 20x certification process.
Rhymetec complements these capabilities with hands-on security and compliance expertise. Our team helps organizations interpret requirements, assess readiness, address security gaps, implement required controls, develop documentation, and prepare for independent assessment.
Additional frameworks supported by Rhymetec and Vanta
Beyond the frameworks listed above, Vanta and Rhymetec support a range of other compliance frameworks and standards. These include ISO/IEC 42001 for AI management systems, DORA for financial sector digital resilience, HITRUST CSF for healthcare security, NIST AI RMF for AI governance, the California Consumer Privacy Act (CCPA), and other global and industry-specific standards.
For the framework or frameworks you select, Rhymetec combines Vanta's compliance automation with hands-on security and compliance expertise to streamline readiness, strengthen your security operations, and establish a program designed for long-term maintenance.
Ready to simplify your Vanta compliance journey?
Compliance should support your business objectives without creating unnecessary operational burden.
Rhymetec combines Vanta's automation with experienced cybersecurity and compliance professionals to manage the work required to build, maintain, and mature your compliance program.
Contact Rhymetec to learn how Vanta and our compliance services can support your organization's security and compliance goals.