The EU AI Act establishes a risk-based regulatory framework for artificial intelligence, creating new requirements for organizations that develop, deploy, distribute, or use AI systems within its scope.
The Act can also apply to organizations outside the European Union. For example, a U.S.-based SaaS company offering AI-powered services to customers in the EU may have obligations under the Act. Organizations developing or deploying AI in areas such as healthcare, recruitment, finance, or critical infrastructure may face additional requirements depending on how their systems are classified and used.
The regulatory timeline has also evolved. The EU's AI Omnibus, which entered into force in July 2026, extended the application timeline for certain high-risk AI requirements. However, other obligations, including Article 50 transparency requirements, remain on their existing timelines.
Penalties for serious violations can reach €35 million or 7% of worldwide annual turnover, whichever is higher, making AI governance and compliance an important consideration for organizations operating in or serving the European market.
This blog covers who falls within the scope of the EU AI Act, how AI systems are categorized, key compliance requirements, the latest implementation timeline, and how frameworks such as ISO/IEC 42001 and the NIST AI Risk Management Framework can support your compliance efforts.
Which types of organizations need EU AI Act compliance?
The EU AI Act can apply to organizations inside and outside the European Union, depending on their role and how their AI systems are placed on or used in the EU market.
Organizations should evaluate their specific role under the Act, as well as the intended purpose and risk profile of their AI systems.
The Act takes a risk-based approach, with different requirements depending on the AI system or practice involved.
Prohibited AI systems: Certain AI practices that pose unacceptable risks are prohibited in the EU. Examples include certain forms of social scoring and specific uses of biometric categorization or emotion recognition.
High-Risk AI systems: AI systems used in areas such as employment, education, critical infrastructure, law enforcement, and access to essential services may be classified as high-risk and subject to extensive requirements. Obligations vary depending on whether an organization is acting as a provider, deployer, or another entity covered by the Act.
AI systems subject to transparency obligations: Certain AI systems must meet transparency requirements. For example, people may need to be informed when they are interacting with an AI system, while certain AI-generated or manipulated content must be identifiable as such.
Minimal or limited-risk AI: Many AI applications, such as spam filters or recommendation systems, face fewer obligations unless another provision of the Act applies.
Organizations that may be impacted include:
AI Developers and providers: Companies developing AI systems or incorporating AI capabilities into their products may have obligations depending on the system, its intended purpose, and their role under the Act.
Deployers of AI systems: Businesses using AI systems within their operations may have obligations around areas such as human oversight, monitoring, and maintaining appropriate records.
Distributors and importers: Organizations placing AI systems on the EU market may have responsibilities to verify that applicable requirements have been met.
Non-EU companies serving EU users: Organizations based outside the EU may still fall within scope when they place AI systems or certain AI-generated outputs on the EU market or use AI systems whose output is used in the EU.
The first step toward EU AI Act compliance is determining whether your organization and AI systems fall within scope, then identifying the specific obligations that apply.
What are the requirements for EU AI Act compliance?
EU AI Act compliance involves a range of governance, risk management, transparency, documentation, and security requirements. The obligations that apply to your organization will depend on your role under the Act and the risk profile of your AI systems.
1. Risk management
Organizations subject to the Act's high-risk requirements need a structured approach to identifying, evaluating, and mitigating risks associated with their AI systems.
A strong risk management program should establish processes for identifying AI-related risks, implementing appropriate controls, monitoring systems over time, and evaluating whether controls remain effective as systems and their operating environments change.
2. Incident response and business continuity
Organizations should have processes for identifying, managing, and responding to incidents involving AI systems.
An effective incident response program defines responsibilities, escalation procedures, communication protocols, and recovery processes. Business continuity planning can also help organizations maintain critical operations when AI systems experience failures, security incidents, or other disruptions.
3. Data governance and protection
AI systems subject to the Act may have requirements around data governance and the quality and suitability of data used to develop and operate them.
Organizations should establish appropriate processes for data management while protecting information from unauthorized access, alteration, corruption, or loss. These requirements can overlap with existing privacy and security programs, including obligations under GDPR.
4. Cybersecurity and ongoing controls
AI systems should be protected against cybersecurity threats and vulnerabilities throughout their lifecycle.
Organizations can support this through controls such as access management, logging and monitoring, vulnerability management, security testing, and anomaly detection. Security controls should evolve alongside the AI systems they protect.
5. Compliance documentation and reporting
Documentation is a central component of AI governance and compliance.
Depending on the system and applicable obligations, organizations may need to maintain records covering areas such as system design, intended purpose, risk management, data governance, testing, monitoring, and performance. High-risk AI systems are subject to additional technical documentation requirements.
A structured documentation program makes it easier to demonstrate how AI systems are governed and how applicable requirements are being addressed.
EU AI Act compliance timeline: what changed in 2026?
The EU AI Act is being implemented in stages, and the timeline was updated in 2026 through the AI Omnibus.
The most significant change affects the application of certain high-risk AI requirements. The extension gives organizations more time to prepare, but it does not eliminate the need to build an AI governance program.
Key EU AI Act dates
February 2, 2025: Prohibitions on certain AI practices and provisions related to AI literacy began applying.
August 2, 2025: Governance provisions and obligations for general-purpose AI models became applicable.
August 2, 2026: Most remaining provisions of the Act apply. This includes Article 50 transparency requirements covering certain AI-generated content and interactions with AI systems. The European Commission has also published guidance to help organizations understand these transparency obligations.
December 2, 2027: Rules for certain high-risk AI systems, including systems used in areas such as employment, education, critical infrastructure, biometrics, migration, and other sensitive areas, will apply.
August 2, 2028: Rules for high-risk AI systems embedded in regulated products, such as certain medical devices, machinery, toys, and lifts, will apply.
The updated timeline gives organizations additional time to prepare for high-risk requirements, particularly as standards and implementation guidance continue to develop. It should not be treated as a reason to delay AI governance.
Organizations should use the additional runway to assess their AI systems, establish governance processes, document risks and controls, and prepare for the requirements that apply to their specific use cases.
The EU AI Act vs ISO/IEC 42001
Organizations building an AI governance program often consider both the EU AI Act and ISO/IEC 42001, but the two serve different purposes.
The EU AI Act is a legally binding regulation that establishes requirements for organizations and AI systems within its scope. ISO/IEC 42001 is an international management system standard designed to help organizations establish, implement, maintain, and continually improve an AI management system.
ISO/IEC 42001 does not replace EU AI Act compliance. However, implementing the standard can provide a structured foundation for addressing many of the governance processes that support compliance.
Where ISO/IEC 42001 and the EU AI Act overlap
Both frameworks emphasize areas such as:
- AI risk management
- Governance and accountability
- Data governance
- Transparency
- Documentation
- Monitoring and continual improvement
- Responsible AI practices
For example, an organization implementing ISO/IEC 42001 may already have processes for identifying AI risks, assigning responsibilities, establishing AI policies, documenting controls, and monitoring the effectiveness of its AI management system.
These processes can help support an organization's EU AI Act compliance efforts.
ISO/IEC 42001 is not a substitute for the EU AI Act
An organization should not assume that implementing ISO/IEC 42001 automatically makes its AI systems compliant with the EU AI Act.
The Act has specific legal requirements based on an organization's role and the AI systems or practices involved. Organizations still need to determine whether the Act applies to their systems and identify any additional requirements that need to be addressed.
The most effective approach may be to build an AI governance program that uses ISO/IEC 42001 as a management framework while mapping applicable controls and processes to EU AI Act requirements.
This allows organizations to build a governance foundation that can support multiple regulatory and customer requirements rather than managing each framework as a separate initiative.
The EU AI Act vs the NIST AI Risk Management framework
The NIST AI Risk Management Framework (AI RMF) is a voluntary framework designed to help organizations manage AI-related risks. It provides guidance across four core functions: Govern, Map, Measure, and Manage.
Unlike the EU AI Act, the NIST AI RMF does not impose legal requirements or establish the same risk classifications.
There is nevertheless meaningful alignment between the two. Organizations using the NIST AI RMF may already have processes for identifying AI risks, establishing governance responsibilities, monitoring systems, and documenting risk-management decisions.
These existing processes can provide a strong foundation for addressing applicable EU AI Act requirements.
In general, organizations with established AI governance frameworks can accelerate their EU AI Act compliance efforts by mapping existing controls and identifying where additional measures are needed.
The goal is not to build each framework independently. It is to create a cohesive AI governance program that can support regulatory obligations, customer expectations, and responsible AI adoption.
5 business benefits of EU AI Act compliance
For organizations operating in or serving the European market, EU AI Act compliance is a regulatory consideration. It can also strengthen the way an organization develops, deploys, and governs AI.
A thoughtful approach to compliance can help organizations build stronger governance, reduce operational risk, and create greater confidence among customers and business partners.
The five key benefits include:
1. Broader access to the EU market
Meeting applicable requirements can help organizations place and deploy AI systems in the EU while reducing the risk of regulatory barriers or enforcement actions.
For businesses building AI-powered products, understanding compliance requirements early can also help avoid significant changes later in the product lifecycle.
2. Reduced risk
AI governance, risk management, transparency, and security controls can help organizations identify and address risks before they become larger operational or regulatory issues.
A structured compliance program can also provide clearer accountability for how AI systems are developed, deployed, and monitored.
3. A stronger position in the market
Demonstrating responsible AI practices can help organizations differentiate themselves as customers, investors, and business partners place greater emphasis on AI governance.
For organizations selling AI-powered products to enterprise customers, the ability to demonstrate mature governance and security can also support procurement and due diligence processes.
4. Stronger AI governance
Building toward EU AI Act compliance can create clearer policies, responsibilities, oversight processes, and documentation around AI.
That foundation can help organizations make more informed decisions as they introduce new AI systems and adapt to evolving regulatory requirements.
5. Greater customer and public trust
Trust is becoming an increasingly important part of responsible AI adoption.
Clear governance, transparency, and security practices give customers and stakeholders greater visibility into how AI is developed and used. Demonstrating that your organization takes these responsibilities seriously can strengthen confidence in your products and services.
Build your EU AI Act compliance program
The EU AI Act establishes a comprehensive framework for managing AI-related risks and responsibilities across the European market. Its requirements vary based on an organization's role, the AI system involved, and the applicable requirements.
The 2026 timeline update gives organizations additional time to prepare for certain high-risk AI obligations, but other requirements are already in effect. Article 50 transparency requirements apply from August 2, 2026, while certain high-risk AI requirements now extend into 2027 and 2028.
For organizations within scope, EU AI Act compliance can involve risk management, data governance, cybersecurity, transparency, incident response, human oversight, and technical documentation. Existing frameworks such as ISO/IEC 42001 and the NIST AI RMF can provide a strong foundation, but organizations still need to assess their specific obligations under the Act.
Not sure where your organization stands? Rhymetec can help you understand your obligations, identify gaps, and build a practical roadmap for EU AI Act compliance. Our experts can help establish the governance, security, and documentation needed to support responsible AI adoption and keep your organization prepared as requirements evolve.
Ready to move forward with your AI governance program? Contact us today.
Artificial intelligence is moving quickly from experimentation to enterprise adoption. Organizations are embedding AI into products, automating workflows, and deploying AI agents that interact with customers, employees, business systems, and sensitive data.
As that adoption grows, so does the need to demonstrate that these systems can be trusted.
Organizations must consider risks that extend beyond traditional application security, including prompt injection, jailbreaks, data leakage, hallucinations, unsafe AI behavior, and the risks that come with AI agents taking actions on behalf of users.
At the same time, customers, partners, regulators, and enterprise buyers increasingly want evidence that organizations are managing these risks responsibly.
This has led to a growing ecosystem of AI standards, frameworks, and regulations. ISO/IEC 42001 provides a framework for establishing an AI management system. The NIST AI Risk Management Framework provides guidance for managing AI risks. Regulations such as the EU AI Act establish legal requirements for organizations developing or deploying certain AI systems.
AIUC-1 is another piece of this landscape.
Designed specifically for AI agents, AIUC-1 combines governance requirements with technical testing to help organizations evaluate and demonstrate the security, safety, reliability, accountability, data privacy, and societal considerations surrounding their AI systems.
What is AIUC-1?
AIUC-1 is an AI assurance standard designed to evaluate how organizations secure, govern, and validate AI agents.
The framework combines operational and governance controls with technical testing. This distinguishes AIUC-1 from approaches that focus primarily on policies or organizational processes. Organizations pursuing certification need to demonstrate that appropriate controls are established and that their AI systems are being technically evaluated against relevant risks.
The current AIUC-1 standard is organized around six foundational principles:
- Data and privacy: Protecting information used or accessed by AI systems.
- Security: Protecting AI systems, models, integrations, and data from unauthorized access and attacks.
- Safety: Reducing the potential for harmful or unintended AI behavior.
- Reliability: Ensuring AI systems perform consistently and within their intended boundaries.
- Accountability: Establishing clear ownership and oversight for AI systems.
- Society: Addressing broader considerations related to transparency, user impact, and responsible AI use.
Together, these principles provide a structured approach for evaluating AI agents across both technical and organizational controls.
AIUC-1 is not intended to replace every other security, governance, or regulatory framework an organization may need to follow. Instead, it provides AI-specific assurance that can complement a broader security and compliance program.
Why was AIUC-1 created?
AI systems introduce risks that traditional security programs were not designed to address on their own.
A conventional application security assessment may evaluate whether an application prevents unauthorized access or protects sensitive data. An AI system requires organizations to consider additional questions:
- Can an attacker manipulate the system through prompt injection?
- Can the AI be persuaded to bypass its intended safeguards?
- Could sensitive information be exposed through an interaction?
- Can an AI agent take an unsafe action through an integrated tool?
- How does the organization respond when an AI system behaves unexpectedly?
- Who is responsible for monitoring and managing AI-related risks?
These challenges become more significant as organizations move from basic generative AI tools toward AI agents that can access information, use external tools, make decisions, and take actions.
Enterprise buyers are increasingly asking for greater transparency into how these systems are secured and governed. Traditional security questionnaires and compliance reports may not fully answer AI-specific questions.
AIUC-1 provides a structured way to address those concerns by combining governance practices with technical validation.
Rather than simply documenting how an organization intends to manage AI, the framework helps evaluate whether appropriate controls are actually implemented and whether AI systems perform as expected under testing.
What does AIUC-1 cover?
The AIUC-1 standard currently contains 50 requirements across its six foundational principles. The specific requirements that apply to an organization depend on the AI agents included within its certification scope.
This means AIUC-1 is not a one-size-fits-all checklist. Organizations first determine which systems are in scope and which requirements apply to those systems.
Areas evaluated can include:
Data and privacy
Organizations need controls for protecting information accessed, processed, or generated by AI systems.
Depending on the system, this may involve data access, privacy, retention, sensitive information, data leakage, and appropriate use of information.
Security
AI agents can introduce new attack surfaces through models, prompts, integrations, APIs, tools, and connected systems.
Security controls help organizations protect these components against unauthorized access, manipulation, and misuse.
Safety
AI systems need safeguards to reduce the risk of harmful or unintended behavior.
Testing and controls may evaluate how an AI system responds to unsafe requests, adversarial inputs, or situations outside its intended use.
Reliability
Organizations need confidence that AI systems behave consistently and within defined boundaries.
This can include evaluating hallucinations, inconsistent outputs, incorrect tool use, failure handling, and other behaviors that could affect the system's intended purpose.
Accountability
AI governance requires clear ownership.
Organizations should be able to establish who is responsible for AI systems, how decisions are documented, how risks are escalated, and how systems are monitored throughout their lifecycle.
Society
AI systems can affect people beyond the organization operating them. AIUC-1 therefore also addresses broader considerations around responsible deployment, transparency, and potential societal impact.
Who should pursue AIUC-1 certification?
AIUC-1 is particularly relevant to organizations developing or deploying AI agents, especially when those systems interact with users, access sensitive information, connect to business applications, or perform actions on behalf of people.
Organizations may want to consider AIUC-1 if they:
- Build AI-powered products or platforms
- Deploy AI agents for customers or employees
- Sell AI solutions to enterprise customers
- Allow AI systems to access sensitive or confidential information
- Connect AI agents to business applications or external tools
- Use AI in business-critical workflows
- Need to demonstrate AI-specific security and governance practices during enterprise procurement
Certification can be especially valuable for organizations selling AI products into larger enterprises. An independent certification can provide customers with additional assurance that the AI system has been evaluated against a defined set of AI-specific requirements.
Ultimately, whether AIUC-1 is appropriate depends on an organization's AI systems, risk profile, customer expectations, and broader regulatory and compliance obligations.
What are the AIUC-1 certification requirements?
AIUC-1 certification starts with defining the systems that will be evaluated.
Organizations identify the AI agents included within their certification scope and determine which requirements apply based on factors such as the agent's capabilities, architecture, integrations, and deployment environment.
This results in a Statement of Applicability that identifies the requirements and controls included in the certification assessment.
From there, organizations need to demonstrate that applicable controls are implemented and supported by appropriate evidence.
Governance and documentation
Organizations may need policies, procedures, risk assessments, ownership structures, and other documentation demonstrating how AI is governed throughout its lifecycle.
Technical controls
AI systems must be evaluated against relevant technical risks. Depending on the system, testing may address areas such as prompt injection, jailbreaks, data leakage, AI agent behavior, tool use, and other AI-specific vulnerabilities.
Operational practices
Organizations also need to demonstrate that AI security and governance practices are operating in practice, not simply documented on paper.
This can include monitoring, testing, incident management, access controls, risk management, and other ongoing activities.
The combination of governance, technical implementation, and operational evidence is central to the AIUC-1 certification process.
How does AIUC-1 certification work?
While the exact process can vary depending on an organization's scope and readiness, certification generally follows a structured path.
1. Define scope
Identify the AI agents and systems that will be included in certification and determine the applicable requirements.
2. Assess readiness
Review existing governance, security controls, documentation, and technical practices to identify gaps before formal assessment.
3. Develop and implement controls
Address identified gaps by establishing policies, processes, technical safeguards, and supporting documentation.
4. Perform technical testing
Evaluate AI systems against applicable technical risks and remediate findings.
5. Prepare for assessment
Organize evidence and documentation and prepare stakeholders for the certification assessment.
6. Complete certification
An authorized certification body conducts the assessment and, when requirements are met, issues the AIUC-1 certification.
7. Maintain certification
Certification is not a one-time exercise. AIUC-1 requires ongoing technical testing and annual recertification to help organizations maintain assurance as their systems and risks evolve.
How long does AIUC-1 certification take?
The timeline depends on the organization's existing security and AI governance maturity, the complexity of the systems being certified, and the gaps identified during readiness.
Organizations with established security programs and mature governance processes may be able to move through certification more quickly than organizations building their AI controls from the ground up.
A readiness assessment can help establish a more predictable timeline by identifying gaps before formal certification activities begin.
The goal should not simply be to move through certification as quickly as possible. Preparing the underlying controls and processes creates a stronger foundation for maintaining AI assurance after certification.
Does AIUC-1 certification need to be renewed?
Yes, AIUC-1 certification is maintained through ongoing technical testing and annual recertification.
This ongoing approach reflects the pace at which AI systems evolve. Models change, applications gain new capabilities, integrations are added, and new attack techniques emerge.
AIUC-1 also evolves with the technology. The standard is updated periodically to reflect changes in AI risks, technology, and the broader regulatory environment.
For organizations, maintaining certification therefore requires an ongoing program rather than a once-a-year compliance exercise.
How does AIUC-1 compare to other AI frameworks?
AIUC-1 is part of a broader AI governance, security, and regulatory landscape. Understanding how these frameworks differ is important because certification against one framework does not automatically satisfy every AI-related requirement.
AIUC-1 vs. ISO/IEC 42001
ISO/IEC 42001 is an international standard for establishing, implementing, maintaining, and continually improving an AI management system.
Its focus is organizational AI governance.
AIUC-1 takes a more AI-specific assurance approach, combining governance requirements with technical evaluation of AI agents.
The frameworks can therefore complement each other. An organization could use ISO/IEC 42001 to establish its broader AI management system while using AIUC-1 to provide additional assurance around specific AI agents and their technical security and reliability.
AIUC-1 vs. NIST AI RMF
The NIST AI Risk Management Framework provides voluntary guidance for organizations managing AI risks.
AIUC-1 differs by providing a defined, certifiable standard with specific requirements and an independent assessment process.
Organizations can use the NIST AI RMF as part of their broader AI risk management strategy while pursuing AIUC-1 for additional AI-specific assurance.
AIUC-1 vs. the EU AI Act
The EU AI Act is a regulation, not a voluntary certification framework.
Organizations subject to the regulation must meet applicable legal requirements based on the AI systems they develop, deploy, or use.
AIUC-1 does not replace those legal obligations. Instead, it can complement an organization's broader regulatory and risk management efforts by providing structured controls and independent assurance around AI systems.
AIUC-1 certification does not automatically mean an organization is compliant with the EU AI Act.

How Rhymetec can help with AIUC-1 certification
AIUC-1 brings together areas that often sit across different teams, including AI governance, cybersecurity, technical testing, documentation, and audit readiness.
Rhymetec helps organizations prepare for AIUC-1 certification while strengthening the broader security and governance practices that support responsible AI adoption.
Our services can include:
- AIUC-1 readiness assessments to identify gaps and establish a certification roadmap
- AI governance support to develop policies, processes, ownership, and risk management practices
- LLM penetration testing to identify AI-specific security vulnerabilities
- Technical control implementation to address identified security and assurance gaps
- Documentation and evidence preparation to support certification activities
- Audit readiness support to prepare for assessment
- Ongoing support for technical testing, control maintenance, and annual recertification
Because AIUC-1 is one component of a broader AI assurance strategy, Rhymetec can also help organizations understand how it fits alongside ISO/IEC 42001, ISO 27001, SOC 2, the NIST AI Risk Management Framework, and applicable AI regulations.
Contact us today to get started.
As organizations move AI from experimentation to production, customers, regulators, and enterprise buyers are demanding greater assurance that AI systems are secure, governed, and operating as intended. To help organizations meet these expectations, Rhymetec is expanding its AI security and governance portfolio with the launch of AIUC-1 Readiness Services.
AIUC-1 is one of the first certification frameworks designed specifically for AI systems and AI agents. It provides a structured approach to evaluating AI across security, safety, reliability, accountability, data privacy, and governance, helping organizations demonstrate that their AI systems meet the expectations of enterprise customers and stakeholders.
Since its launch in 2025, AIUC-1 has continued to develop as an emerging standard for AI assurance. In 2026, Schellman became the first authorized auditor for the framework, establishing a pathway for independent evaluation and certification for organizations pursuing AIUC-1.
With this new offering, Rhymetec provides end-to-end guidance throughout the AIUC-1 certification journey, helping organizations prepare for assessment while strengthening the security and governance practices that support long-term AI adoption.
Supporting the Next Generation of AI Assurance
Enterprise AI introduces new opportunities alongside new risks. As organizations deploy AI-powered products, copilots, and autonomous agents, they must address evolving concerns around model security, prompt injection, hallucinations, data protection, governance, and ongoing oversight.
AIUC-1 brings these technical and operational requirements together into a single certification framework. Rather than replacing established standards like ISO/IEC 42001, ISO 27001, SOC 2, or the NIST AI Risk Management Framework, AIUC-1 complements them by focusing specifically on the unique risks introduced by AI systems.
Rhymetec's AIUC-1 services help organizations:
- Assess readiness for AIUC-1 and identify gaps.
- Develop AI governance policies and supporting documentation.
- Implement security and operational controls aligned to AIUC-1 requirements.
- Prepare evidence and documentation for assessment activities.
- Coordinate assessment readiness activities.
- Support ongoing compliance requirements and annual recertification.
"Our customers are moving quickly with AI, but trust has become just as important as innovation. Organizations need practical guidance that helps them secure AI systems while demonstrating responsible governance to customers, partners, and regulators. AIUC-1 represents an important step toward creating greater confidence in enterprise AI, and we're excited to help organizations prepare for the framework."
— Kyle Jones, Chief AI Officer, Rhymetec
Addressing the Next Generation of AI Risk
AIUC-1 was developed in response to the rapid evolution of AI systems from tools that generate content to systems capable of making decisions and taking actions on behalf of users. As these technologies become more integrated into business operations, organizations are seeking clearer ways to validate that AI systems are secure, reliable, and governed appropriately.
The framework establishes a structured approach to evaluating AI systems across key areas such as security, safety, reliability, accountability, and data privacy. By combining technical evaluation with operational governance, AIUC-1 helps organizations demonstrate that responsible AI practices extend beyond policy into the way AI systems are designed, tested, and maintained.
Building on Rhymetec's AI Security Expertise
The launch of AIUC-1 Readiness Services expands Rhymetec's growing portfolio of AI security offerings, which includes AI governance consulting, ISO/IEC 42001 readiness, AI risk assessments, and AI penetration testing.
By combining governance expertise with offensive security testing and compliance advisory services, Rhymetec helps organizations build AI programs that are not only innovative, but secure, resilient, and prepared for increasing customer and regulatory scrutiny.
As enterprise adoption accelerates, organizations are looking for trusted partners who can help them operationalize responsible AI without slowing innovation. AIUC-1 provides an emerging framework for demonstrating that commitment, and Rhymetec is helping customers navigate every stage of their readiness journey.
Organizations interested in preparing for AIUC-1 can learn more about Rhymetec's AI security services or contact our team to discuss their AI governance and readiness goals.
While approximately 88% of organizations have deployed artificial intelligence within at least one business function, only 8% maintain a comprehensive framework to oversee it. As organizations scale their artificial intelligence capabilities, traditional information security paradigms must adapt to meet new architectural demands. When product teams embed large language models (LLMs), pull data through dynamic retrieval pipelines, or deploy autonomous workflows, they inherit entirely new operational liabilities.
Securing modern AI applications extends far beyond protecting static codebases. It involves managing systems defined by non-deterministic behavior, where a model can return variant outputs to the exact same prompt, alongside unique challenges like input logic vulnerabilities, unintended data exposure, and unconstrained API interactions.
Rather than serving as an administrative constraint, robust compliance functions operate as a critical commercial accelerator. Implementing practical AI governance solutions builds the institutional trust required to unlock enterprise revenue, clear complex procurement hurdles, and expand operations with complete confidence. Brakes don't exist to slow you down; they exist so you can take tight corners faster and with complete control.
To expand into enterprise markets without the guesswork, organizations need proactive AI compliance solutions that translate complex global regulations into clean, rapid development workflows.
The New Operational Reality: Defining AI Governance
Effectively implementing these frameworks requires a clear understanding of what modern governance entails and how the baseline for system risk has transformed.
What Is AI Governance?
At its core, AI governance is the proactive framework of corporate policies, internal accountability, and active validation mechanics that keep your AI systems predictable and secure. It isn’t a passive paper drill or a legal checkbox; it’s a living operational system designed to ensure your models perform strictly within your business parameters.
Why the Urgency Has Accelerated
The transition from legacy software infrastructure to generative architectures has completely redrawn the standard security perimeter.
- The Non-Deterministic Shift: Legacy information security was built to protect deterministic code, systems where explicit logic reliably yields the same output every time. Generative AI changes the rules. Because models respond dynamically to natural language, they are vulnerable to input manipulation and data exposure that classic firewalls simply cannot catch.
- Autonomous Authority and Agentic Risk: Teams are rapidly moving past simple chatbots into complex, agentic ecosystems. When you give non-human actors the autonomy to ingest data, query internal databases, and execute tool calls across your production environment, you inherit an entirely new tier of liability.
- The Commercial Demand for Trust: Enterprise buyers, general counsels, and institutional investors are no longer checking boxes based on verbal assurances. Globally, four out of five organizations now face direct customer inquiries regarding their AI risk management practices. Demonstrating structured, verifiable oversight has become the absolute baseline requirement for closing high-value commercial contracts.
Velocity Meets Verification: Mapping the Modern AI Risk Surface
True oversight requires balancing top-down organizational governance (the policies) with proactive technical validation and testing. When executed properly, these elements unify into complete AI security solutions that safeguard your intellectual property while accelerating your engineering timeline.
Here is how the leading frameworks, compliance standards, and testing methodologies map out for your business:
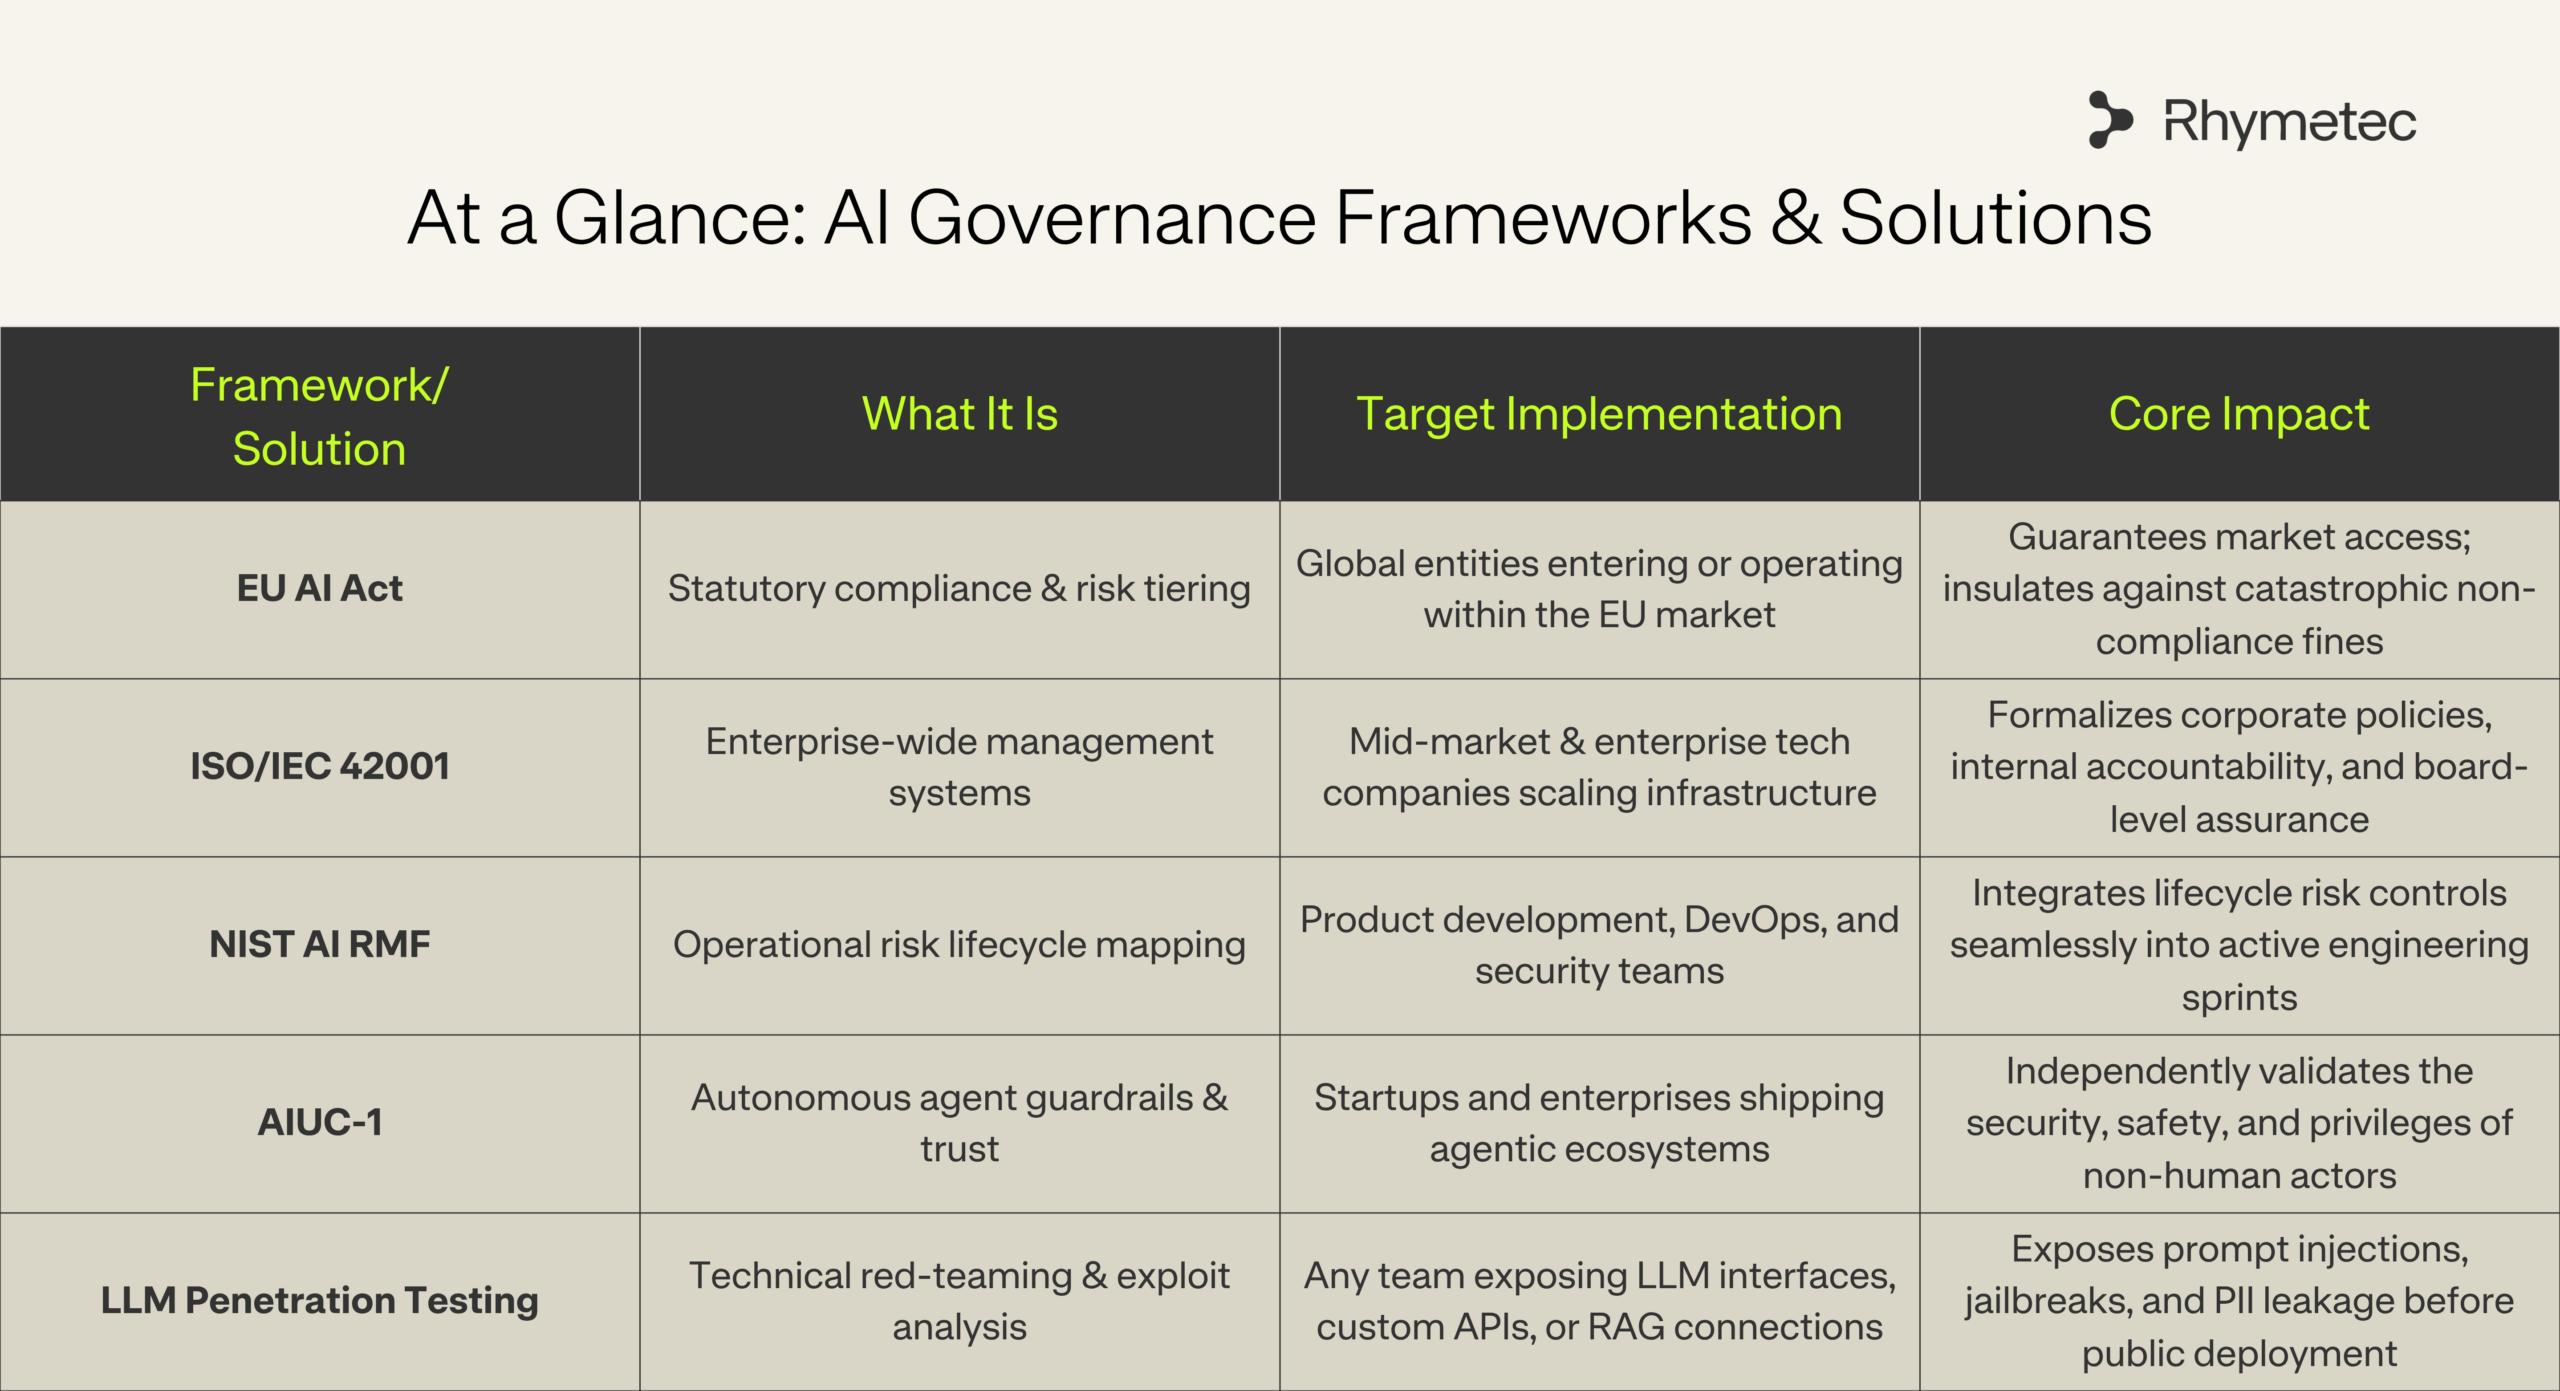
EU AI Act: Securing Global Market Access
The EU AI Act enforces a strict, risk-based classification system that groups artificial intelligence applications into four tiers: unacceptable, high, limited, and minimal risk. Applications that cross the line into unacceptable risk are banned entirely, while high-risk setups are subject to deep transparency mandates, incident logging, and continuous data management.
A Critical Distinction on Scope: Similar to the EU’s General Data Protection Regulation (GDPR), the EU AI Act applies to any organization globally if their AI system is deployed within the EU, supplied to the EU market, or leverages data that impacts individuals living inside the EU, whether or not that organization is in the EU. If your product has a global footprint, you are within its jurisdiction.
Turning Regulatory Pressure into a Commercial Engine
Adhering to the EU AI Act is a core requirement for operating in global economic hubs. Non-compliance carries severe financial exposure, with penalties reaching up to €35 million or 7% of a company’s global annual turnover (whichever is higher).
Provisions prohibiting unacceptable AI practices are already in effect, and the remaining requirements continue to take effect on a phased timeline. While certain high-risk AI deadlines have been extended, transparency obligations remain scheduled for August 2, 2026. Enterprise buyers are actively purging vendors who cannot provide definitive proof of compliance. Meeting these criteria means your organization can bypass complex legal questionnaires, outpace legacy competitors, and win enterprise contracts faster.
Structural Architecture: ISO 42001 and the NIST AI RMF
Scaling modern software platforms requires flexible, elite frameworks that provide organizational structure without adding administrative friction.
- ISO/IEC 42001: As the world’s first formal international standard for artificial intelligence management, ISO 42001 provides the blueprint for an Artificial Intelligence Management System (AIMS). It defines structural accountability, continuous oversight, and data control policies, proving to investors and enterprise boards that your infrastructure is highly disciplined.
- NIST AI RMF: While ISO/IEC 42001 establishes the overarching management system for organizational accountability, the National Institute of Standards and Technology’s framework provides the granular, tactical blueprint needed to operationalize risk management across the daily development lifecycle. Structured around four continuous functions, Govern, Map, Measure, and Manage, it translates abstract risk concepts into practical, daily engineering checkpoints that map to standard workflows.
AIUC-1: The New Frontier for Agentic AI Systems
As artificial intelligence moves rapidly from passive chat boxes to autonomous, agentic systems capable of executing multi-step workflows, traditional security benchmarks drop away. This operational shift demands AIUC-1 (Artificial Intelligence Unified Controls), the definitive compliance standard engineered specifically for autonomous AI agents that interact with core enterprise databases, application layers, and software integrations.
Understanding Agentic Risk
When an autonomous agent experiences logic manipulation, inherits broad API access, or triggers cascading downstream automated actions without a human-in-the-loop, it introduces significant data and corporate liabilities.
"Traditional firewalls protect static code, but they are entirely blind to the non-deterministic logic of an autonomous AI agent.
The moment you grant a non-human actor the authority to query enterprise databases and execute workflows, your risk surface shifts from predictable vulnerabilities to dynamic liabilities. If your compliance framework hasn't evolved to match that autonomy, you're flying blind."
— Kyle Jones, Chief AI Officer, Rhymetec
AIUC-1 targets this specific exposure layer through 51 comprehensive controls distributed across 6 core pillars:
- Data & Privacy: Preventing unauthorized retraining loops, PII exposure, and IP leakage.
- Security: Implementing continuous execution logging, explicit access parameters, and active defenses against jailbreaks.
- Safety: Mandating independent validation and strict human-in-the-loop overrides for high-consequence agent actions.
- Reliability: Stress-testing against hallucinated data outputs and unconstrained third-party tool executions.
- Accountability: Establishing undeniable lines of operational ownership for every autonomous system action.
- Societal Impact: Actively monitoring and identifying algorithmic or behavioral bias within deployed models.
Because agentic ecosystems evolve rapidly alongside fast-paced release cycles, AIUC-1 moves away from traditional annual audits in favor of a continuous validation model. Achieving and maintaining certification requires independent penetration testing and technical review conducted at least once every quarter.
This rolling cadence ensures that model guardrails, retrieval pipelines, and third-party tool access remain secure against changing adversarial threats.
Where high-level standards like ISO 42001 evaluate company-wide management procedures, AIUC-1 operates at the use-case execution level to deliver the ongoing technical validation required by legal and procurement teams.
LLM Penetration Testing: Translating Governance into Technical Validation
Policies, procedures, and documentation establish your structural defense, but LLM penetration testing is what proves whether your actual code and system guardrails stand up to active, malicious pressure. True governance requires continuous real-world validation; you cannot responsibly claim to govern an AI system if you lack clear visibility into how it handles a deliberate attack.
Traditional web application security focuses on infrastructure flaws like cross-site scripting (XSS) or SQL injection. Modern AI cybersecurity solutions focus entirely on the non-deterministic logic of the model, conversational routing, prompt structure, vector databases, and retrieval-augmented generation (RAG) connections.
Adversarial Validation Phases
A premium testing engagement maps directly to the OWASP Top 10 for Large Language Model Applications, broken down into four execution phases:
- Planning and Preparation: Mapping your specific deployment landscape, defining foundational base models (e.g., GPT, Gemini, Claude), system prompts, authentication barriers, plugin permissions, and data-use boundaries.
- Discovery and Enumeration: Tracing internal data pipelines, conversational routing, API endpoints, and vector database structures to map exactly how contextual data is ingested, retrieved, and processed.
- Exploitation and Validation: Utilizing automated red-teaming scripts paired with expert manual jailbreaking to push for prompt injection, sensitive data/PII extraction, insecure output handling, and model denial of service (DoS).
- Reporting and Remediation Guidance: Delivering a clean, executive-ready breakdown of validated exploits, clear severity ratings, and prescriptive code adjustments to permanently secure your application guardrails.
Do you need independent testing if you use an enterprise foundational model? Yes. While the base infrastructure of models provided by providers like OpenAI or Anthropic is highly secure, your unique implementation layer, your custom instructions, RAG parsing architecture, system plug-ins, and data access workflows, creates entirely new vulnerabilities. If a malicious input can force your custom application to execute unauthorized actions, the base model’s default safety parameters cannot protect your environment.
Move Forward with Assurance
Whether your company is a SaaS platform embedding AI features into an existing application, a startup scaling an LLM prototype into rapid production, or an enterprise expanding into highly regulated markets, implementing modern AI security solutions shouldn't come at the cost of your development velocity.
By pairing proactive technical testing with robust, practical corporate frameworks, you eliminate the guesswork from AI adoption. Rhymetec helps you build the safety guardrails you need to push boundaries safely, satisfy regulators efficiently, and prove to your customers that you take responsibility as seriously as speed.
Ready to validate your security posture and streamline your path to compliance? Contact us today.
With 88% of organizations now using AI in at least one business function, the race to innovate has never been faster. But as these applications scale, they drastically expand the web application attack surface. Without the right security frameworks, deploying generative AI can introduce severe model, prompt, and integration risks that traditional security tools simply weren't built to catch.
This guide breaks down what every organization needs to know about LLM penetration testing, how it differs from standard security assessments, and how to build a resilient AI ecosystem that supports compliance and growth.
What Is LLM Penetration Testing And Why Is It Different?
LLM penetration testing is a specialized security assessment designed to evaluate how generative AI systems behave under adversarial conditions.
Traditional web application penetration testing was designed to uncover vulnerabilities like SQL injection, cross-site scripting (XSS), and server misconfigurations. It focuses heavily on static infrastructure.
LLM penetration testing evaluates the logic, behavior, and integration layers of generative AI systems. Traditional automated scanners like Burp Suite or Nessus were not designed to test the probabilistic nature of AI. Instead of attacking the infrastructure alone, LLM testing uses adversarial tactics to manipulate prompts, bypass guardrails, and attempt sensitive data extraction.
To understand the scope of an LLM penetration test, it helps to break down the core components of the AI ecosystem:
- The Model: The underlying backend intelligence (e.g., Claude, OpenAI, Gemini).
- The Agent: An API-hooked action the AI can perform, such as sending an email, querying a database, or creating a support ticket.
- The Message Prompt: The user-facing text input, which serves as the primary entry point for most attack vectors.
Even if you are utilizing a highly secure, third-party foundational model, your specific implementation layer, like system prompts, plugins, agents, and data handling workflows, creates new points of exposure.
The Regulatory Push for AI Security
Compliance frameworks and international regulations are rapidly catching up to generative AI. Security is no longer just a best practice; it is a legal requirement.
The EU AI Act is already fundamentally shifting how companies approach AI risk. With Article 5 prohibitions in effect and the strict compliance deadline for high-risk models looming on August 2, 2026, companies handling EU resident data must prove their AI systems are safe, unbiased, and secure.
In addition to European regulations, comprehensive LLM penetration testing supports emerging governance frameworks like the NIST AI Risk Management Framework (AI RMF) and ISO/IEC 42001. Delivering structured reporting that demonstrates validated safety testing is now a prerequisite for passing enterprise procurement reviews and maintaining executive confidence.
Top AI Vulnerabilities You Need to Assess
A robust LLM penetration test aligns directly with the OWASP Top 10 for Large Language Model Applications. Because LLMs are probabilistic, meaning the exact same prompt can generate different answers on different days, testing requires highly manual, creative, and persistent adversarial prompt engineering.
A thorough assessment should target these critical vulnerabilities:
- Prompt Injection: The most common attack vector, where an attacker uses clever wording to bypass instructions, override guardrails, or force the system to execute unintended commands.
- Sensitive Information Disclosure: Manipulating the model to reveal restricted content, PII, or sensitive data about other users.
- System Prompt Leakage: Tricking the AI into revealing its own backend instructions, guardrails, or safety features, allowing attackers to map out loopholes.
- Vector Embedding Weakness (RAG Assessments): Exploiting a Retrieval Augmented Generation (RAG) pipeline to force the AI to retrieve unauthorized internal data.
- Unbounded Consumption: Testing system limits to ensure an attacker cannot abuse the AI to trigger massive cloud infrastructure costs or a Denial-of-Service (DoS) state.
How Rhymetec Approaches LLM Penetration Testing
At Rhymetec, our methodology combines adversarial prompt engineering, automated red-teaming, and expert manual logic validation to assess risk across your entire generative AI lifecycle. Each engagement aligns with the OWASP Top 10 for Large Language Model Applications, ensuring your testing reflects the latest standards in generative AI security.
Rather than a one-size-fits-all approach, we scope our testing to match your specific AI architecture:
Evaluating Core Models and Chat Interfaces: For standard public-facing or internal assistants, we focus heavily on foundational vulnerabilities. Using manual, creative prompt injection, we test the system's resilience against sensitive data leakage, system prompt extraction, and unbounded consumption attacks aimed at exhausting your cloud resources.
Assessing RAG Pipelines and Internal Knowledge Bases: If your application retrieves contextual data from an internal database (Retrieval-Augmented Generation), the stakes are significantly higher. We conduct deep-dive assessments to identify vector embedding weaknesses, ensuring your system cannot be manipulated into bypassing guardrails to access or expose compartmentalized proprietary data.
Validating Agents and Integrations: As your AI ecosystem grows, so does your attack surface. We thoroughly evaluate agentic workflows, such as API-hooked actions that allow the AI to send emails, query databases, or create tickets, to ensure tool and plugin access stays strictly within intended controls.
Expanding the Scope: To ensure complete security from the database to the chat interface, we highly recommend pairing your LLM assessment with a standard Web Application Penetration Test. This guarantees that your surrounding implementation layer does not become the weak entry point for attackers.
Insights That Speed Up Innovation
Your AI systems deserve more than surface-level testing. By actively hunting for prompt injection, jailbreak risks, and guardrail evasion before public exposure, you can strengthen trust in your customer-facing AI systems without degrading performance.
At the end of a Rhymetec engagement, you receive an executive presentation and a comprehensive report featuring validated prompt-based exploits, prioritized severity ratings, and prescriptive remediation guidance.
Looking for LLM Penetration Testing Services? We can help.
Accelerate your AI deployment without compromising security. Contact Rhymetec to learn how our LLM Penetration Testing services can secure your generative AI architecture and keep your innovation moving forward.
Artificial intelligence is accelerating software development and reshaping the security expectations that surround it. Developers are shipping code faster than ever, often with the assistance of AI tools.
However, this same technology has also changed the economics of attacking software. Adversaries are using AI to lower the cost of reconnaissance and iterate through exploits at scale.
In a recent webinar hosted by Rhymetec and XBOW, Christian Mouer, Director of Offensive Security at Rhymetec and Bill Nichols, Head of Customer Success at XBOW explored how an AI-powered penetration testing model allows organizations to increase testing velocity, validate real attack paths faster, and gain broader visibility across modern applications, while maintaining the depth and context required for meaningful risk reduction.
Why Traditional Penetration Testing Timelines No Longer Match Modern Development
Many organizations still rely on annual or semi-annual point-in-time tests, an engagement begins, a snapshot is taken, and a report is delivered weeks later. That approach worked when applications changed slowly and release cycles were measured in quarters.
Today, development moves continuously. New features, endpoints, and integrations are introduced on a weekly, sometimes daily, basis. By the time a traditional test is completed, the environment it assessed has already evolved.

To keep pace, defenders cannot simply scale humans linearly with software output: it is cost and time-prohibitive. This is where autonomous offensive security comes in.
From Theoretical Exposure to Proven Exploitability
One of the most consistent pain points for security teams is the volume of unverified findings produced by automated tools. Large scan outputs require significant internal effort to determine what is real, what is exploitable, and what actually matters to the business.
The approach demonstrated in the webinar prioritizes validation. Exploits are executed against the live environment, attack paths are confirmed, and results are correlated before they are ever delivered.
That shift changes the nature of the final report. Instead of a backlog of potential issues, organizations receive a focused set of confirmed vulnerabilities with clear evidence of impact.
“Hypotheses are cheap. Proof isn’t. We don’t surface a finding unless the system can validate that it’s real.” — Bill Nichols, XBOW
For security and engineering teams, this significantly reduces the time spent reproducing issues and allows remediation efforts to begin immediately.
Expanding Coverage Without Extending Engagement Length
Application ecosystems have grown far beyond a single web interface. Modern environments include large API surfaces, multiple user roles, third-party integrations, and complex authorization logic.
Manually mapping and testing that entire landscape within a standard engagement window forces difficult tradeoffs. Teams must choose between depth in a few areas or lighter coverage across the whole application.
Autonomous execution removes that constraint. Continuous attack surface mapping and parallel exploit testing allow a far greater portion of the environment to be assessed in the same timeframe.
“It’s another pen tester on the team. If we work together, we're able to cover so much more ground than we would have otherwise." — Christian Mouer, Rhymetec
This expanded coverage is what makes deeper, human-led analysis possible later in the engagement.
Reallocating Human Expertise to High-Value Security Work
When the most time-intensive phases of testing, such as reconnaissance, enumeration, and initial exploitation, are handled autonomously, the role of the tester changes.
Instead of spending the majority of the engagement identifying entry points, offensive security experts are able to focus on:
- Chaining multi-step attack paths
- Analyzing real business impact
- Validating complex authorization scenarios
- Working directly with developers on practical remediation strategies
“When we’re cutting down that investigative time, it gives us additional days to validate, find more vulnerabilities, and explore more deep-dive attack paths.” — Christian Mouer, Rhymetec
This is where the greatest risk reduction occurs and where human experience delivers the most value.
The Hybrid Approach: Why AI Doesn't Replace Humans
A common misconception about AI powered penetration testing is that it aims to replace human testers. In practice, the model works as an extension of the testing team rather than a substitute for it.
While XBOW can map an attack surface and execute exploits 24/7, it lacks the business context and nuance that a Rhymetec offensive security expert provides.
Business Logic and Context
AI might flag that a user can see all emails in a system. However, a human tester understands the context: if that user is an HR Administrator, that access is intended. Rhymetec’s team supplies the critical business logic to ensure findings are relevant to the organization's specific operations.
Complex Remediation
Finding a bug is only half the battle. Fixing it without breaking the application is the other half. Rhymetec provides the "human element" of advising on remediation strategies that align with the client’s tech stack and resources.
Parallelism and Depth
The ideal workflow involves running XBOW in parallel with manual testing.

Real-World Impact: Speed and Scalability
The combination of XBOW’s automation and Rhymetec’s expertise delivers results that were previously difficult to obtain in both timeline and scope.
During the webinar, the team shared a case study of a massive web application containing approximately 650 endpoints.
- Traditional Timeline: A thorough manual test would typically take 10 to 15 business days.
- AI-Accelerated Timeline: The XBOW agent mapped and tested the environment in roughly 48 hours.
This acceleration allowed the Rhymetec team to spend the remaining time validating complex findings and exploring deep-dive attack paths that the AI surfaced, ultimately delivering a comprehensive report in five days rather than three weeks.
“We’re able to turn around that pen test confidently within five business days rather than going 10 to 15 days out.” — Christian Mouer, Rhymetec
In Conclusion: AI as a Force Multiplier
As 76% of CISOs anticipate a material cyber attack in the next 12 months, the need for speed and accuracy in testing has never been higher.
Rhymetec’s AI-Powered Penetration Testing partnership with XBOW offers the perfect balance of intelligence and intuition. By automating the reconnaissance and vulnerability identification phases, we allow our certified penetration testers to focus on what they do best: validating impact, analyzing business risk, and guiding remediation.
Key Benefits of the Rhymetec x XBOW Partnership:
- Accelerated Timelines: Reduce testing time from weeks to days.
- Reduced Noise: AI-driven validation eliminates false positives common in traditional scanners.
- Deeper Coverage: Test vast attack surfaces and thousands of endpoints simultaneously.
- Actionable Intelligence: Receive reports validated by expert human testers, not just automated logs.
Contact us to learn more about how to integrate AI-powered testing into your security strategy.
Watch the Full Webinar
Deepak Chopra once said, "All great changes are preceded by chaos." This has never been more accurate than when it’s applied to the current AI and cybersecurity environments—and the regulations that govern them.
New frameworks like the Digital Operational Resilience Act (DORA), the EU AI Act, the Network and Information Systems Directive 2 (NIS2) and the Cybersecurity Maturity Model Certification (CMMC) are reshaping how businesses handle security, risk and compliance. These regulations aren't just about ticking boxes—they carry major financial penalties and demand real operational changes.
For companies in financial services, AI development, critical infrastructure or defense, staying ahead of the changes is vital to avoid penalties, protect data and maintain trust. Let's look at what each entails.
DORA: Protecting Financial Institutions From Cyber Disruptions
Financial institutions face constant cyber threats and operational risks. DORA aims to empower financial organizations to weather system disruptions and continue operating smoothly.
DORA requires penetration testing, vulnerability assessments and disaster recovery planning. It focuses on business continuity to ensure that if a system fails, a plan is in place to keep operations running. Banks, insurance companies and investment firms must validate security controls through rigorous testing.
This regulation is a wake-up call for financial institutions to take cybersecurity resilience seriously. The penalties for non-compliance are severe, making it crucial for businesses to invest in robust security testing and operational risk management.
The EU AI Act: Setting The Global Standard For AI Compliance
AI development currently operates in a regulatory gray area, but the EU AI Act is changing that. One of the first laws to set clear boundaries on AI usage, it focuses on ethical risks, security concerns and prohibited applications.
The most important takeaway is the significant financial penalties for non-compliance: These can be up to 7% of a company's global annual revenue or 35 million euros, whichever is higher. That's more than GDPR, which has already forced businesses worldwide to rethink their approach to data privacy.
This law explicitly bans certain AI applications, particularly those that exploit vulnerabilities. The ban includes AI-powered cyberattacks, social manipulation and unethical facial recognition practices. Article 5 of the act outlines prohibited AI uses, such as systems that exploit people's age, disabilities or socioeconomic circumstances.
This isn't simply a privacy factor; its purpose is to prevent AI from being weaponized.
A common misconception is that this law only affects European companies. That's not the case. Any company developing, deploying or processing AI systems in the EU—or serving EU customers—must comply. For example, if a U.S. company hosts its platform in an EU data center or processes European customer data, this regulation applies.
The EU AI Act is setting the stage for global AI governance. Similar regulations are expected to emerge worldwide, making it smart for businesses to adapt now rather than scrambling to comply later.
NIS2: Strengthening Cybersecurity For Critical Infrastructure
Also in the EU, the NIS2 Directive expands cybersecurity requirements for critical industries like energy, healthcare, transportation and digital services. It builds on the original NIS Directive but goes much further, applying to more organizations, increasing security expectations and enforcing stricter penalties.
The enhanced reporting requirements are one of the biggest challenges. Companies must notify regulators of cyber incidents within 24 hours, provide a complete assessment within 72 hours and demonstrate they are actively managing security risks.
The directive also emphasizes stronger supply chain security, holding companies responsible for ensuring their vendors meet cybersecurity standards. This means businesses can't just secure their own systems—they must also vet suppliers and partners to prevent weak links in the supply chain.
Beyond reporting and supply chain oversight, NIS2 enforces stricter governance requirements. Organizations must appoint security officers, conduct regular risk assessments and develop robust cybersecurity policies. Those that fail to comply face heavy financial penalties and increased regulatory scrutiny.
Compliance isn't optional for companies operating in or serving the EU market. NIS2 is setting a new cybersecurity standard, and businesses that don't act risk fines, operational disruptions and reputational damage.
CMMC: Raising the Bar For U.S. Defense Contractors
The CMMC is a requirement for companies working with the U.S. Department of Defense (DoD). It builds on cybersecurity frameworks like NIST 800-171, ensuring that defense contractors follow strict security protocols to protect sensitive government data.
Recent changes to CMMC include a new self-assessment option for Level 1 compliance, making it easier for smaller contractors to meet requirements without hiring third-party auditors. However, higher certification levels still require independent verification, adding layers of accountability.
With the new compliance requirements going into effect in mid-2025, businesses need to act now. The DoD has made it clear that CMMC certification will be mandatory for contracts, and companies that don't comply risk losing business.
Evolving Security Frameworks: A Smarter Approach To Compliance
For organizations handling sensitive data in healthcare, finance and other regulated industries, new security frameworks present a way to prove compliance with strict privacy and cybersecurity standards. In the past, certification required a lengthy, one-size-fits-all assessment, but newer models offer more flexible options with fewer controls, reducing complexity while maintaining security.
Many businesses don't realize that certification levels vary, and choosing a lower-tier option may not meet regulatory or customer expectations. This is especially important for HIPAA compliance, where recognized certifications can demonstrate that companies meet security standards. As cybersecurity laws evolve, understanding these frameworks ensures that businesses stay compliant, competitive and prepared for future regulations.
Laws like DORA, the EU AI Act and NIS2 are designed to keep technology from becoming a threat. AI development currently lacks clear rules—without oversight, it can be used in dangerous ways. These regulations force businesses to prioritize security and ethics upfront, preventing bigger problems down the road.
To stay ahead, organizations must:
- Identify relevant regulations and update security policies.
- Invest in risk assessments, penetration testing and employee training.
- Stay informed—more regulations are coming.
Compliance isn't just about avoiding penalties but about building a safer, more resilient digital future. Companies that act now will lead, while those that wait will fall behind.
You can read the original article posted in Forbes by Rhymetec CISO, Metin Kortak.
About Rhymetec
Our mission is to make cutting-edge cybersecurity available to SaaS companies and startups. We've worked with hundreds of companies to provide practical security solutions tailored to their needs, enabling them to be secure and compliant while balancing security with budget. We enable our clients to outsource the complexity of security and focus on what really matters – their business. Contact us today to get started.
Artificial intelligence (AI) is increasingly shaping cybersecurity. While it brings opportunities, it also raises concerns. For chief information security officers (CISOs), understanding AI can mean the difference between turning it into a valuable asset or fearing it as a threat.
Here's how you can make AI a trusted ally in your operations by implementing actionable strategies for safe and effective use.
AI in Cybersecurity—Friend or Foe?
AI can be both a friend and a foe in cybersecurity. One primary concern for CISOs is privacy. When employees use AI without proper training, sensitive information might be exposed. According to IBM's 2024 Cost of a Data Breach report, 57% of IT professionals surveyed cited data privacy as a leading barrier to implementing generative AI models.
Another risk is that attackers will use AI to create sophisticated threats, making it a double-edged sword. There are also fears about AI replacing jobs, but this is not necessarily true. When effectively managed, AI helps automate repetitive tasks and enhances security efficiency. The key lies in using AI ethically, and proactively managing its risks.
Prerequisites for Embracing AI Safely
Before embracing AI, CISOs must ensure foundational protections are in place. Preventative measures like data privacy controls and intrusion detection systems are essential for preventing worst-case scenarios.
Training is another essential piece. Employees need to be well-informed about how to use AI tools correctly—particularly generative AI tools such as chatbots, which could be used carelessly to expose sensitive data. Training should focus on what information can and cannot be shared with AI systems.
In addition, aligning with established frameworks like ISO 42001 or the NIST AI Standards provides CISOs with clear guidelines. Aligning with these standards helps reduce incidents by 30%, according to the NIST 2023 AI Security Report, enabling a safe environment for integrating AI and setting up controls that reduce risks and foster trust.
AI as a "Force Multiplier" for CiSOS
AI can be a powerful "force multiplier" for security teams. AI-based threat detection reduces incident response times by up to 50%, allowing CISOs to detect threats early on and respond more quickly. When used correctly, it significantly increases efficiency. One of the key advantages of AI is its ability to perform log analysis and threat detection. It can sort through massive amounts of data that would be impossible for human teams to analyze manually.
AI also assists employees directly. AI-driven tools answer policy questions, saving time and boosting internal training effectiveness. This doesn't reduce jobs, but instead shifts the focus to strategic activities that add value.
How to Deploy AI with Human Oversight and Accountability
Human oversight is essential when integrating AI into cybersecurity. Teams must conduct random checks on AI's outputs to identify biases and inaccuracies, ensuring AI aligns with organizational goals. Accountability also needs to be well-defined. Even though AI plays a role in decision-making, humans are still ultimately responsible. CISOs should assign accountability to specific teams or individuals who oversee AI deployments to ensure that the organization has a clear plan for dealing with any mistakes or misuse of AI systems.
Continuous AI Improvement in Cybersecurity
Continuous improvement is necessary to keep AI effective. Training exercises like phishing simulations help employees stay vigilant. Developers should receive specialized training on building ethical AI systems, including AI System Impact Assessments to gauge the societal impact of technologies. AI tools also need regular evaluation for biases and effectiveness to ensure they meet evolving organizational needs.
AI Limitations in Cybersecurity
Despite all the benefits, AI has its limitations in cybersecurity. AI depends heavily on the quality of its training data, so its decisions will reflect those weaknesses if the data it is trained on is incomplete or biased. It's also not yet capable of handling every kind of security scenario; many tasks still require human intuition and understanding.
AI is simply a tool that does what it's trained to do. It lacks the ability to think critically or understand nuance. Because of this, CISOs must be realistic about what AI can achieve and ensure that it is always paired with human oversight to fill in the gaps where AI falls short.
Actionable Tips to Integrate AI without Fear
For CISOs looking to integrate AI into their security operations without the fear of unintended consequences, it's best to start small. Begin with low-risk processes like automated log analysis and build from there. Collaboration is also key; work with AI experts to choose and implement the best tools suited to the organization's needs.
Before scaling up AI usage, conduct internal audits and gap analysis to understand any weak spots. This helps prepare the organization for full AI integration while ensuring all necessary security controls are already in place.
Making AI your Best Friend
When adopted thoughtfully and carefully, AI can transform cybersecurity operations, making them more efficient and effective. CISOs should start with small steps, focusing on robust training, human oversight, and incremental adoption. AI doesn't need to be feared—it needs to be understood and managed. With proper safeguards, AI can be a powerful ally in keeping organizations safe from cyber threats.
You can read the original article posted in Fast Company by Rhymetec CISO, Metin Kortak.
About Rhymetec
Our mission is to make cutting-edge cybersecurity available to SaaS companies and startups. We've worked with hundreds of companies to provide practical security solutions tailored to their needs, enabling them to be secure and compliant while balancing security with budget. We enable our clients to outsource the complexity of security and focus on what really matters – their business. Contact us today to get started.
Interested in reading more? Check out more content on our blog.
This ISO 42001 checklist will walk you through the four phases of achieving certification.
These steps are based on our security team's process for helping organizations complete their ISO/IEC 42001 certification readiness. Our security team at Rhymetec has helped hundreds of companies achieve their security goals and meet compliance requirements. To find out how we can fast-track you to ISO 42001 compliance, contact our team today:
Hopefully, this checklist will give you a clear idea of the work ahead needed for ISO 42001 compliance and will help you create a project plan.
We'll start with a high-level overview of your ISO 42001 checklist and then dive into each phase in detail:
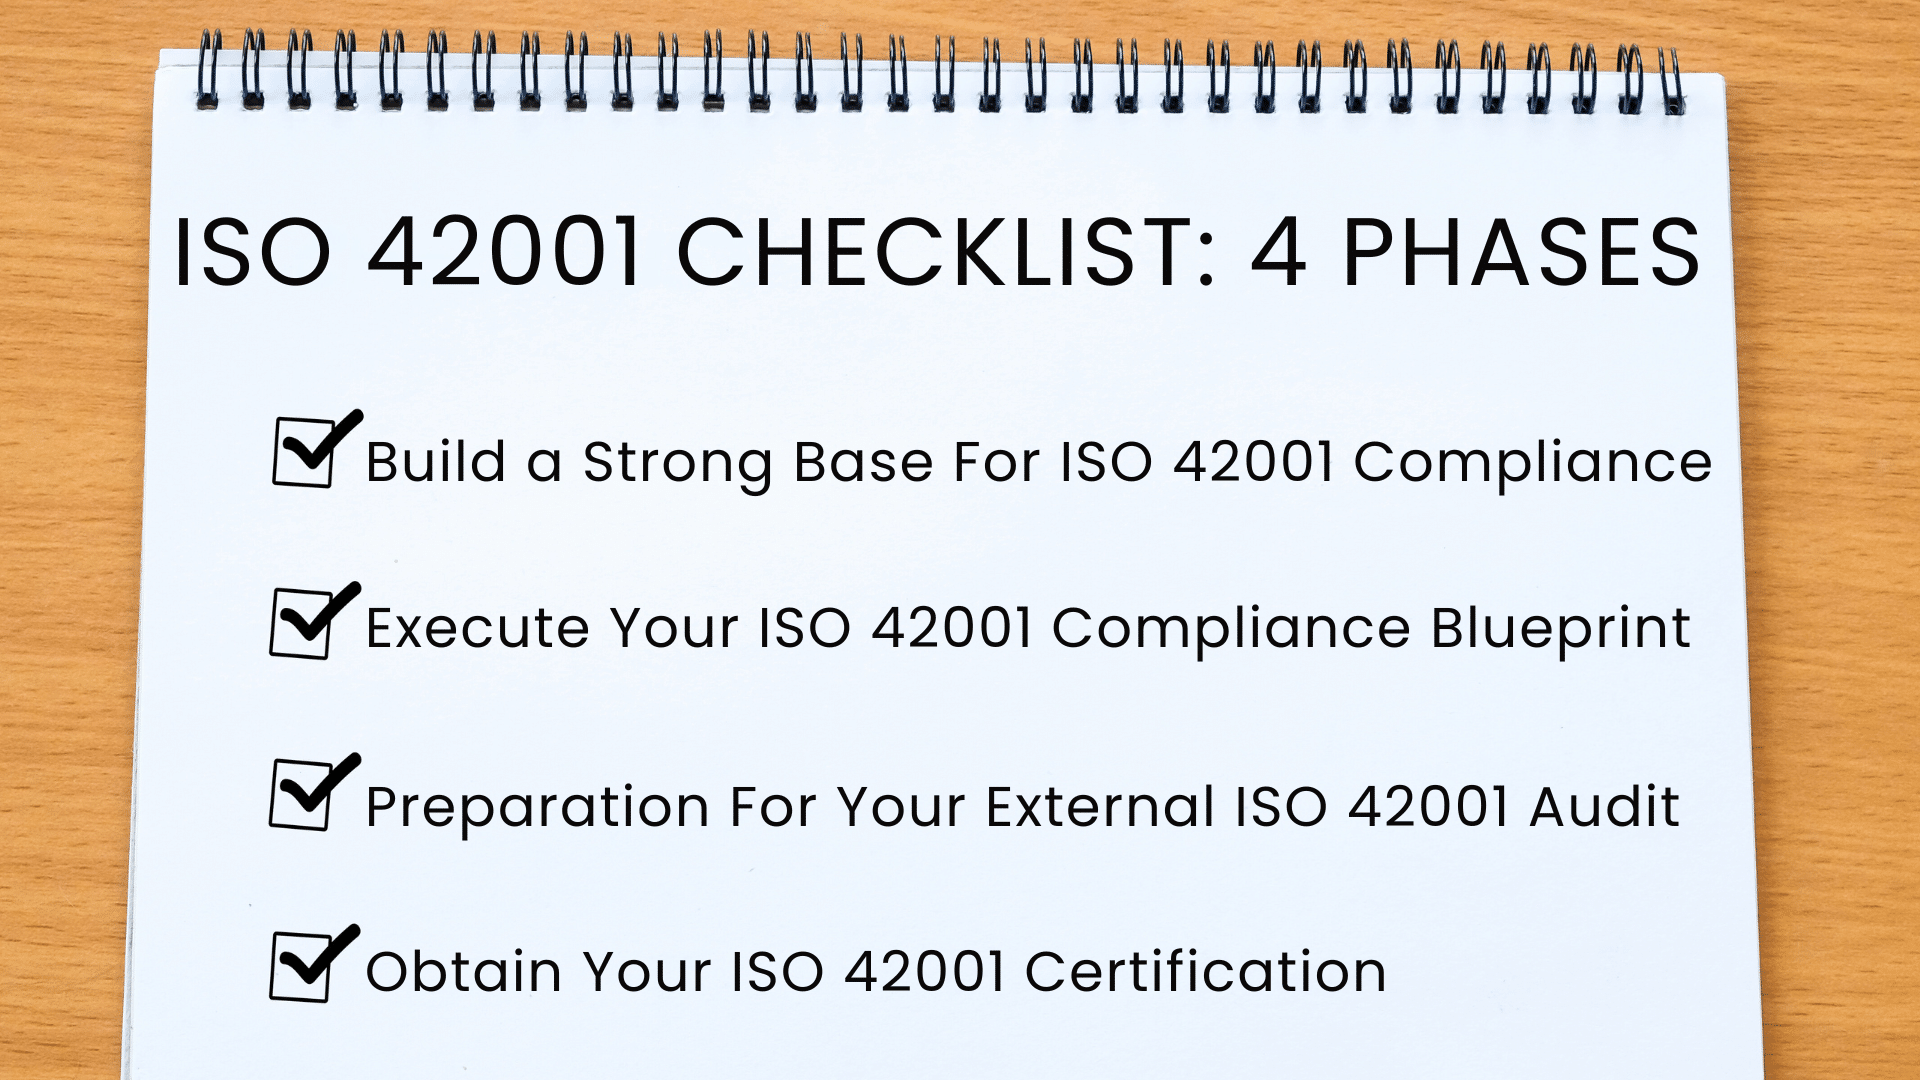
ISO 42001 Checklist Overview
1. Build a Strong Base for ISO 42001 Compliance.
- Understand Your ISO 42001 Requirements
- Conduct An Initial Gap Analysis
- Conduct A Risk Assessment
- Obtain Executive Support
2. Execute Your ISO 42001 Compliance Blueprint.
- Designate a Compliance Project Leader
- Draft An Implementation Roadmap For AIMS
- Set Up The AIMS Structure
- Create Organization-Wide Awareness
- Apply Necessary AIMS Controls
- Conduct Executive AIMS Evaluations
3. Preparation for Your External Audit.
- Conduct Internal Audits
- Select an ISO 42001 Certification Body
- Prepare Documentation
- Pre-audit Meeting
4. Obtain Your Certification.
- Undergo Your Audit
- Address Any Identified Issues
- Ongoing Improvements & Post-Audit Plan
Let's go over detailed steps under each phase:
Phase 1: Build A Strong Base For ISO 42001 Compliance
In this phase, you'll lay the groundwork for your organization to build an Artificial Intelligence Management System (AIMS) and achieve ISO 42001 compliance.
Establishing an AIMS is not just about compliance; it's about crafting a concrete strategy to improve decision-making and risk management around AI technologies. After this phase, you'll have a clear direction for responsible AI use and be on the right path to work towards ISO 42001 compliance:
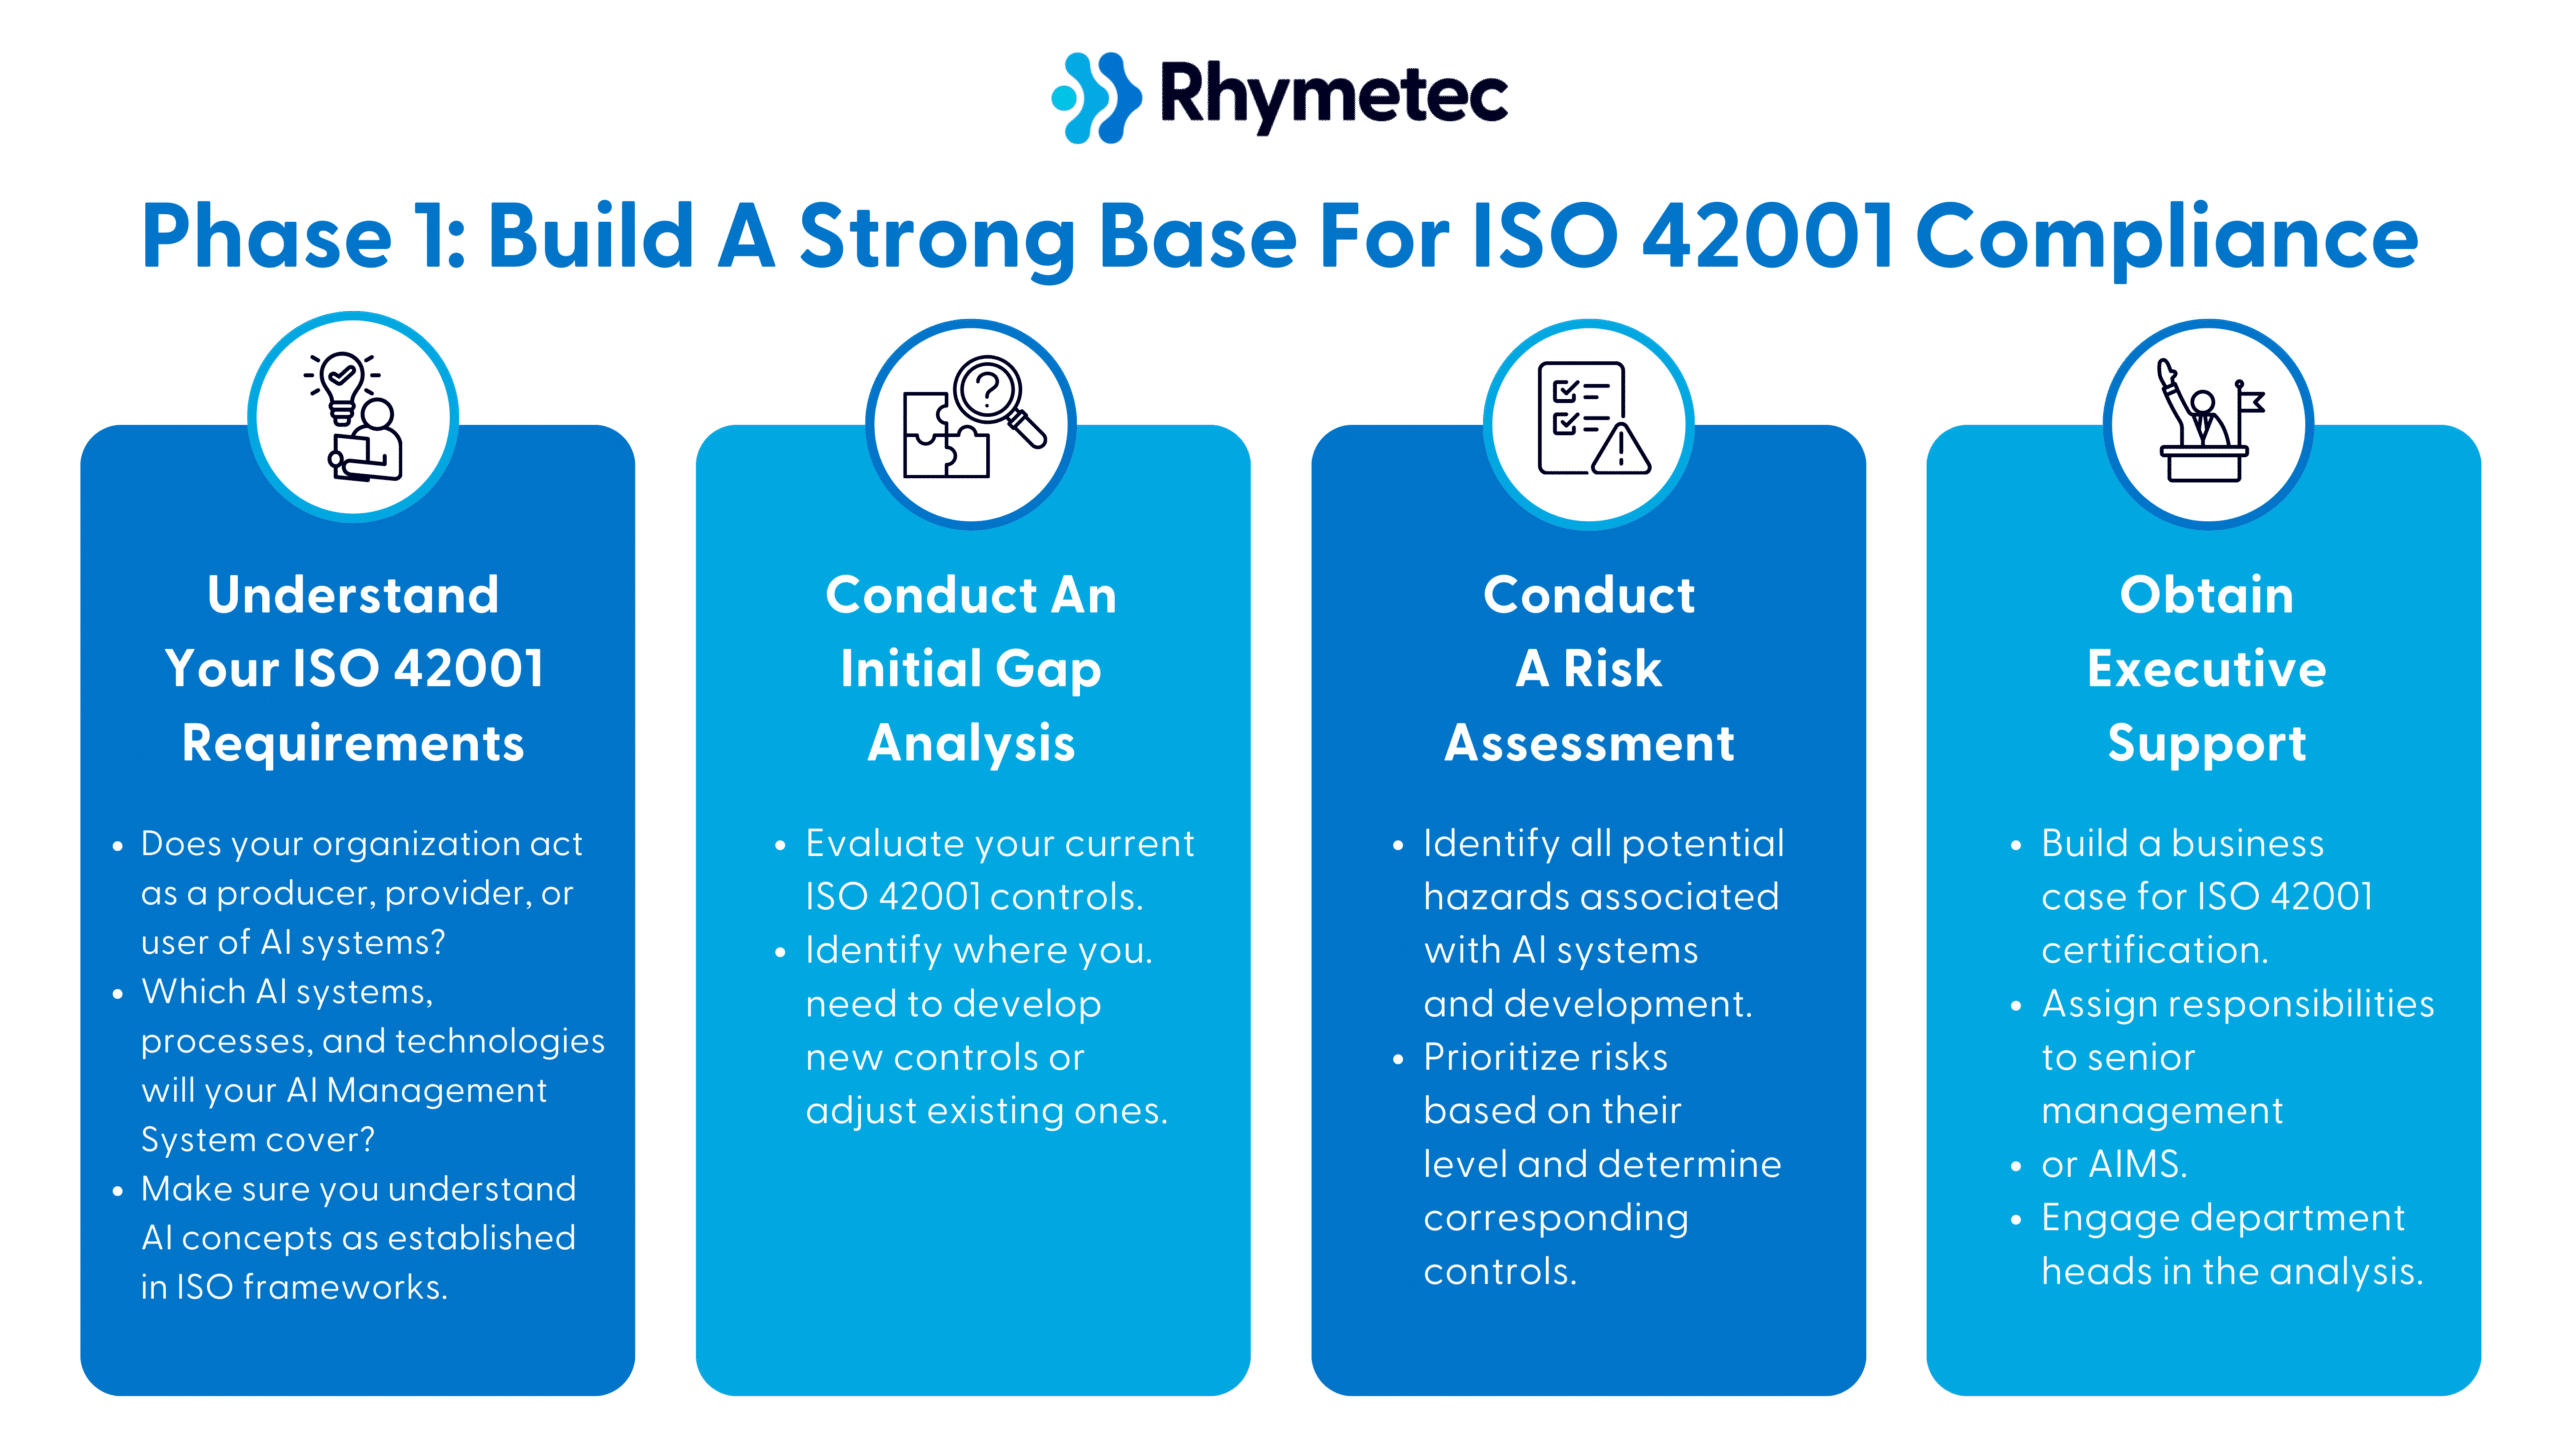
1. Understand Your ISO 42001 Requirements
Does your organization act as a producer, provider, or user of AI systems?
You'll have different requirements depending on which of these your organization falls under.
Providers are companies such as OpenAI that build AI models like ChatGPT. Service providers customize and use these models. Users can include any business that uses AI services either directly from producers or via services from providers.
Which AI systems, processes, and technologies will your AI Management System cover?
Which technologies and assets do you have that incorporate AI? You will need to identify what will be included to map out the boundaries of your Artificial Intelligence Management System (AIMS).
Make sure you understand AI concepts as established in ISO frameworks.
Are you already familiar with how ISO frameworks define terms like "AI systems" and "machine learning models"?
If so, great! If not, ISO provides a glossary of terms you can use to see exactly what the frameworks mean when they use these terms. It's important to familiarize yourself with the terminology to understand each step of the compliance process, speak the same language as your auditors, and avoid miscommunications.
2. Conduct An Initial Gap Analysis
Evaluate your current ISO 42001 controls.
Compare your existing practices against ISO 42001 controls. Do you have any current practices to mitigate AI risks? What about ethical concerns related to AI, and data integrity concerns? You may already have a basis for some of the controls, especially if you already have another ISO framework.
Identify where you need to develop new controls or adjust existing ones.
Now that you have an idea of how your current practices map onto ISO 42001 controls, draft up a complete list of what you need to do to develop new controls or adjust existing ones. You will need this going forward.
3. Conduct A Risk Assessment
Identify all potential hazards associated with AI systems and development.
Unlike frameworks like ISO 27001, ISO 42001 does not focus heavily on security.
Security is an element of the framework, but a relatively small one. Instead, the potential hazards associated with AI, such as ethical issues, environmental considerations, and concerns around fairness and bias, are key.
Focusing on the areas mentioned above, come up with a list of potential AI risks related to your products, services, and all other activities.
Prioritize risks based on their level and determine corresponding controls.
Assess the likelihood and potential consequences of each risk. You will need this documentation later on. Start drafting an action plan to remediate risks, focusing on the highest risks first. Assess your list of existing practices and their effectiveness in mitigating risks.
Threats range from cybersecurity attacks to operational risks like system failures or errors in the AI's decision-making process. For each AI-related risk that your organization could potentially encounter, the impact level needs to be assessed:
Impact is categorized as low, medium, or high based on factors like financial loss, legal repercussions, and damage to customer trust. As an example, if your AI handles sensitive or critical data, the risk of a data breach would be considered high risk (as a breach could result in substantial legal and reputational damage).
A medium risk could be data bias in functions that are not critical to core operations but could impact user satisfaction or minor decision-making processes. A threat with a low-risk level could be any potential minor AI performance fluctuations. If you use an AI-driven customer support chatbot, for example, the risk of users experiencing minor delays in response time or slight inaccuracies in non-critical responses could be considered low risk.
Think ahead when conducting your risk assessment: What would happen if your organization experienced each risk? How complex would remediation be? How would employees, stakeholders, and your business operations be impacted?
4. Obtain Executive Support
Build a business case for ISO 42001 certification.
Create a compelling business case that shows the strategic benefits of ISO 42001 certification. Include how it will enable AI governance, help your organization comply with regulations, ease concerns that customers and prospects may have, and build stakeholder trust.
A formalized AI management system offers a lot of long-term value. What this looks like will depend on your specific organization. Try to emphasize not only the ways in which ISO 42001 mitigates risk but also how it offers opportunity and innovation potential.
Assign responsibilities to senior management for AIMS.
Assign senior management responsibilities to align the AIMS with your goals and provide them with the necessary resources.
Engage department heads in the analysis.
Bringing in department heads from IT, legal, operations, and human resources into the gap analysis process, for example, is a great way to create engagement across the organization. Plus, their involvement ensures all potential impacts of AI systems are being considered.
ISO 42001 Checklist Phase 2: Execute Your ISO 42001 Compliance Blueprint
Here, you'll activate the plans laid out above. This phase involves hands-on tasks such as appointing a project manager, setting up the structures for your AIMS, and implementing controls. This phase of your ISO 42001 checklist ends with your internal audit to assess your ISO 42001 certification readiness before moving on to external evaluations:
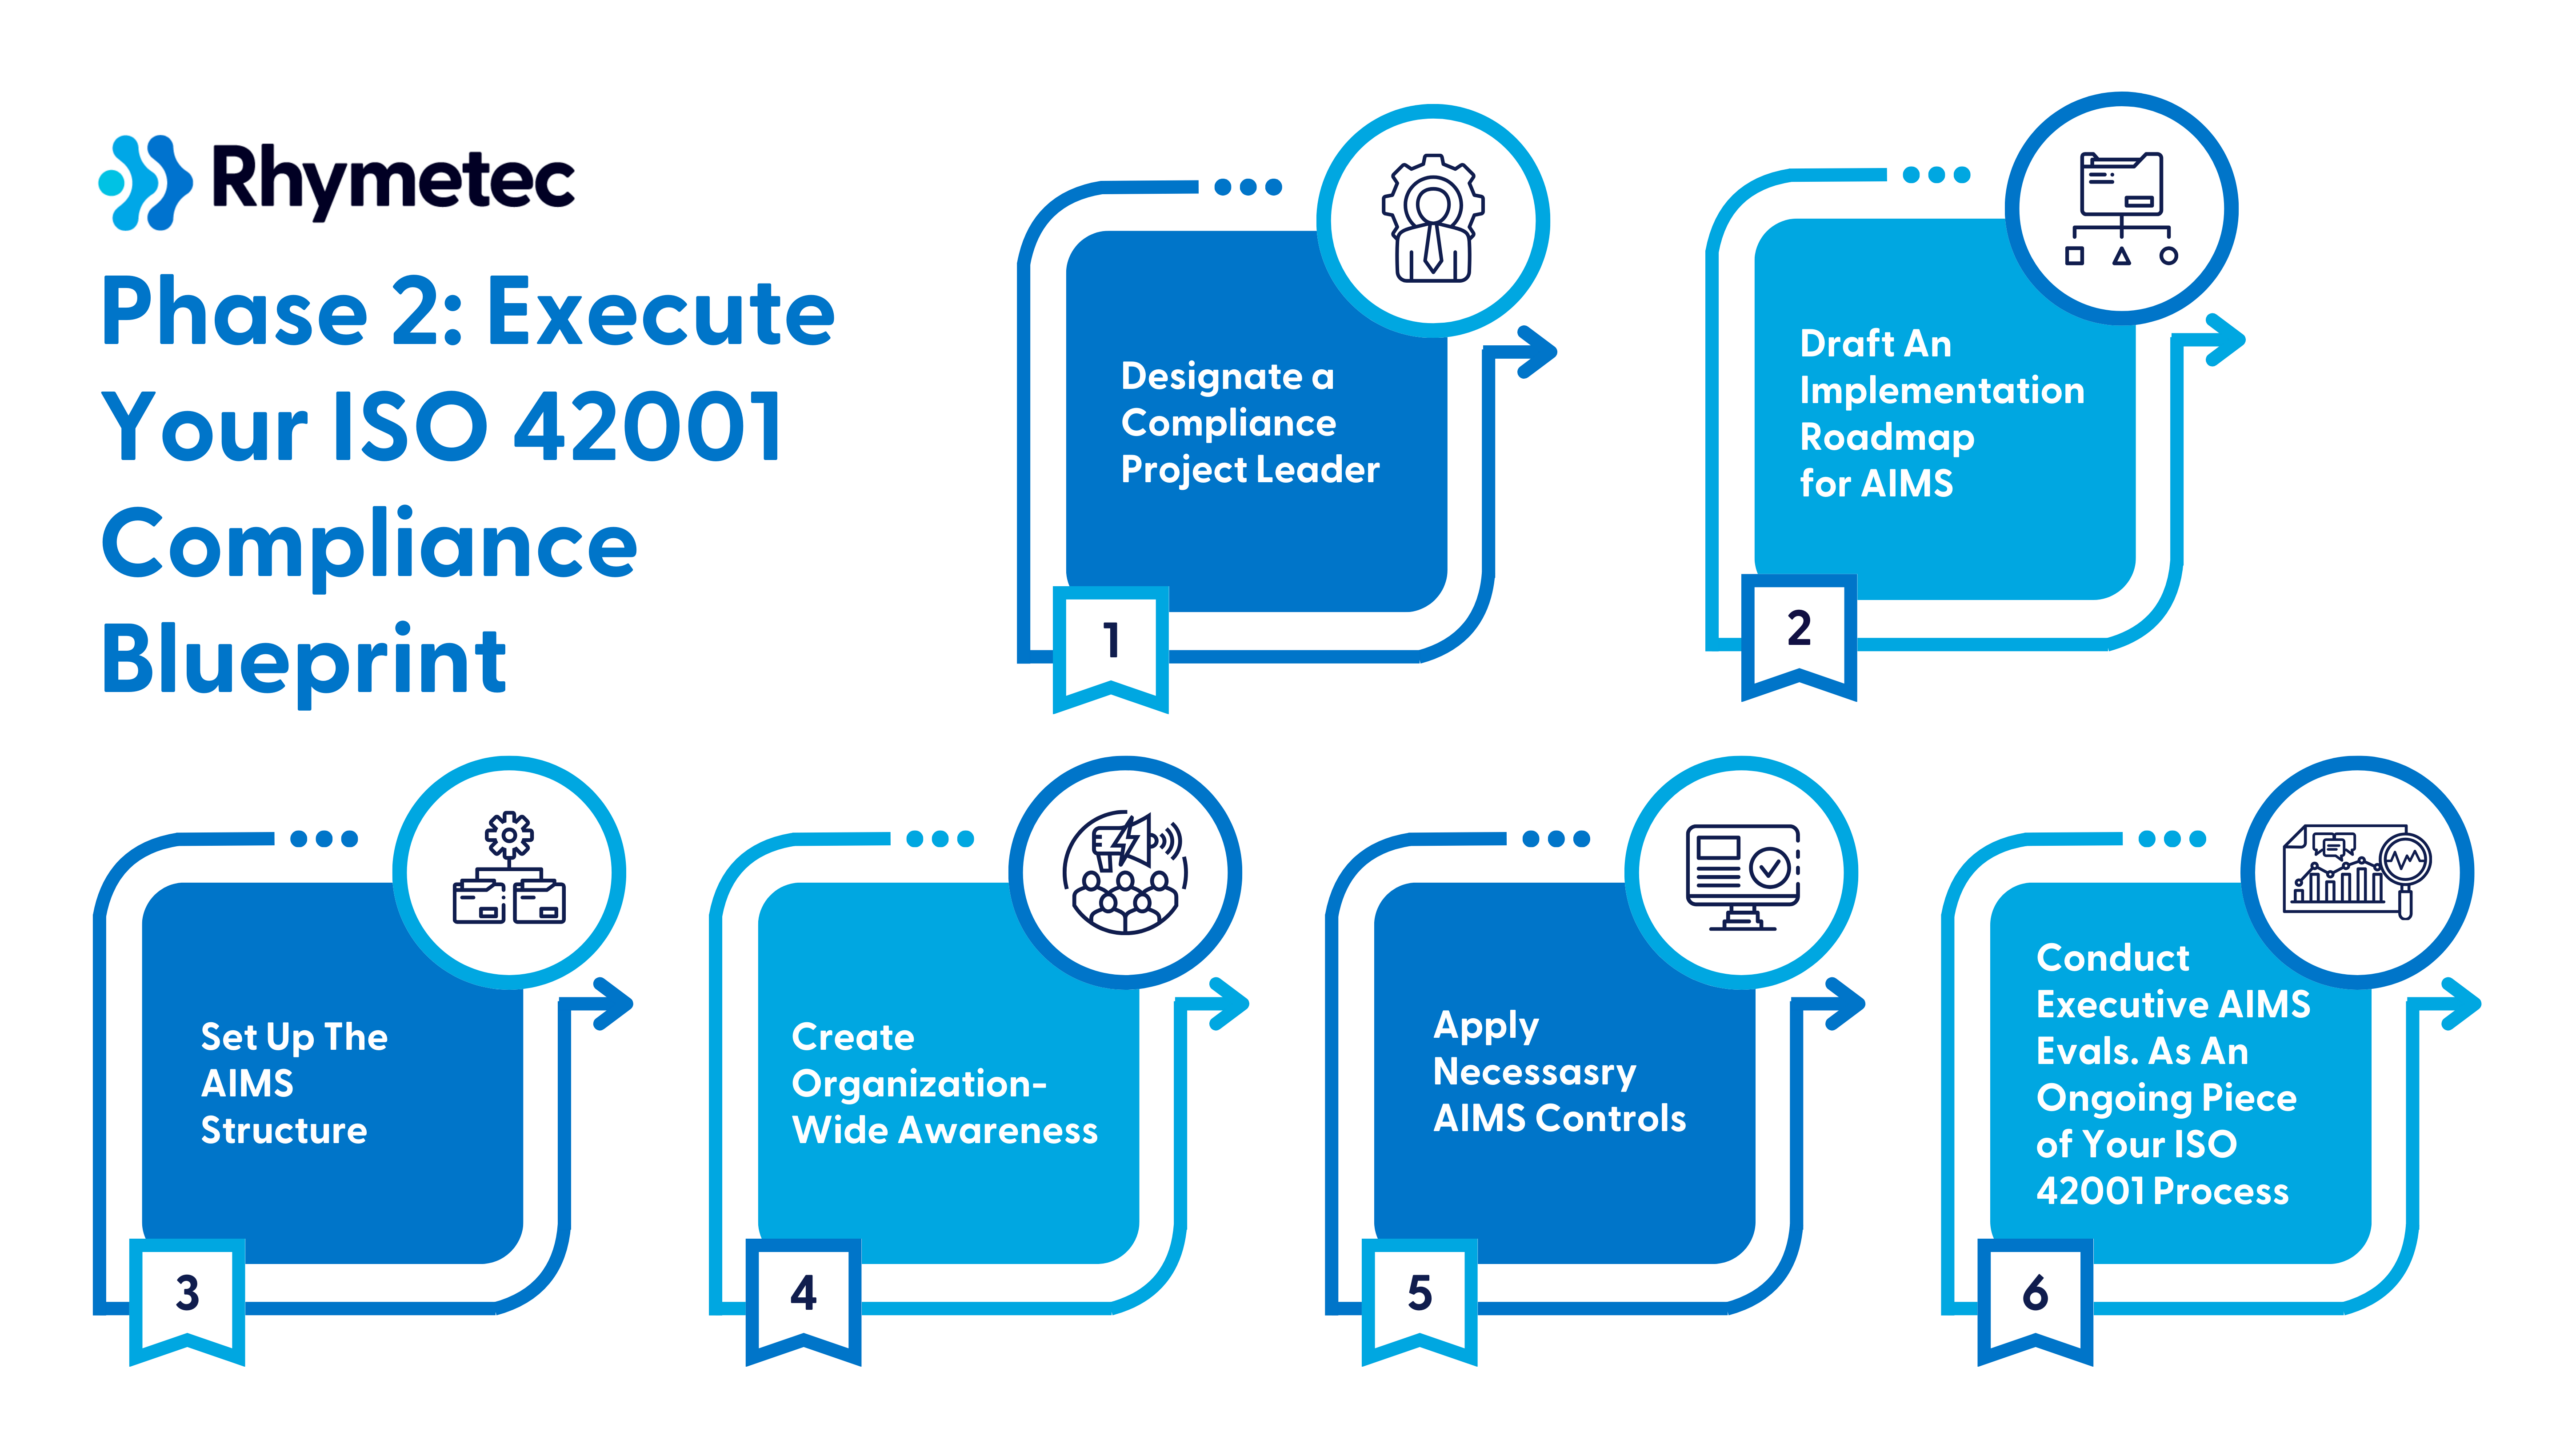
1. Designate a Compliance Project Leader
Select a qualified compliance leader.
Appoint a project manager with a solid understanding of AI and compliance issues. This individual will coordinate all activities related to achieving ISO 42001 certification and act as the point of communication between departments and external auditors.
2. Draft An Implementation Roadmap For AIMS
Develop a detailed project plan for your ISO 42001 process.
Solidify your project plan using the gap analysis conducted earlier as a baseline. Your plan should include deadlines, resource allocations, and every stage from the initial assessment to the final audit.
Budget appropriately.
Allocate sufficient financial and human resources to support the project. This includes funding for training, external consultants, auditing costs for certification, and technology upgrades needed to comply with ISO 42001.
*TIP: When implementing ISO 42001, you should not rely on checklists alone from external sources. Purchasing the standard should be in your budget for successful implementation.
3. Set Up The AIMS Structure
Define Your AI Management System Structure.
Set up a structure for your AIMS that integrates with existing organizational processes. The structure should support all stages of AI lifecycle management, from development to deployment and maintenance.
Document All Processes.
Make sure you are documenting everything as you work through these steps. You'll need everything from workflows, decision-making processes, and control measures documented when it comes time for your audit.
*TIP: Using a compliance automation tool at this point can be tremendously helpful. Compliance automation platforms allow you to easily organize your documentation. When it comes time for your audit, it makes your auditor's job easier and more efficient to be able to see everything clearly laid out in one central place.
4. Create Organization-Wide Awareness
Develop training programs.
Organize training sessions to improve your employees' AI and compliance knowledge base. Focus on ethical AI use, data security, and the legal implications of AI technologies.
Circulate information across the organization.
Distribute informational materials and regular updates about AIMS and its importance to encourage organization-wide understanding and engagement. Internal communications channels such as newsletters, intranets, and staff meetings are all good avenues for dissemination.
5. Apply Necessary AIMS Controls
Implement controls.
ISO 42001 controls address risk management, data protection, system reliability, and transparency.
The way controls are implemented will vary depending on your organization's industry, needs, risks, and the types of AI applications you use. (A complete control list can be found in ISO/IEC 42001:2023, Annex A).
*TIP: Consulting with a compliance expert at this step may be necessary. Many startups choose to work with a Managed Security Services Provider (MSSP) at this stage. Rhymetec's vCISO program provides hands-on managed security services, taking the complexity of compliance off your plate, and doing the readiness and audit phases for you.
Plan to regularly update control measures.
Continuous improvement is required by ISO 42001. You should plan to continuously monitor and update controls to adapt to new technologies, changes in organizational processes, and shifts in regulatory requirements.
6. Conduct Executive AIMS Evaluations As An Ongoing Piece of Your ISO 42001 Process
Organize regular review meetings.
Hold management review meetings periodically to assess the AIMS' performance. Reviews should involve top management and key stakeholders to help AI systems & applications align with broader organizational goals.
Update your executive team regularly.
The last step in this phase of your ISO 42001 checklist is to regularly update your executive team. Keep them informed about the outcomes of management reviews, including challenges, achievements, and the effectiveness of the AIMS.
ISO 42001 Checklist Phase 3: Preparation for External ISO 42001 Audit
This stage is where you make sure everything is in perfect order for your audit.
Choosing the right auditor is critical - you want to choose a reputable certification body that will conduct a legitimate and fair audit, providing credible validation of your AIMS.
Each step in this phase is also an opportunity to solidify stakeholder confidence and demonstrate your proactive approach to responsible AI management and compliance.
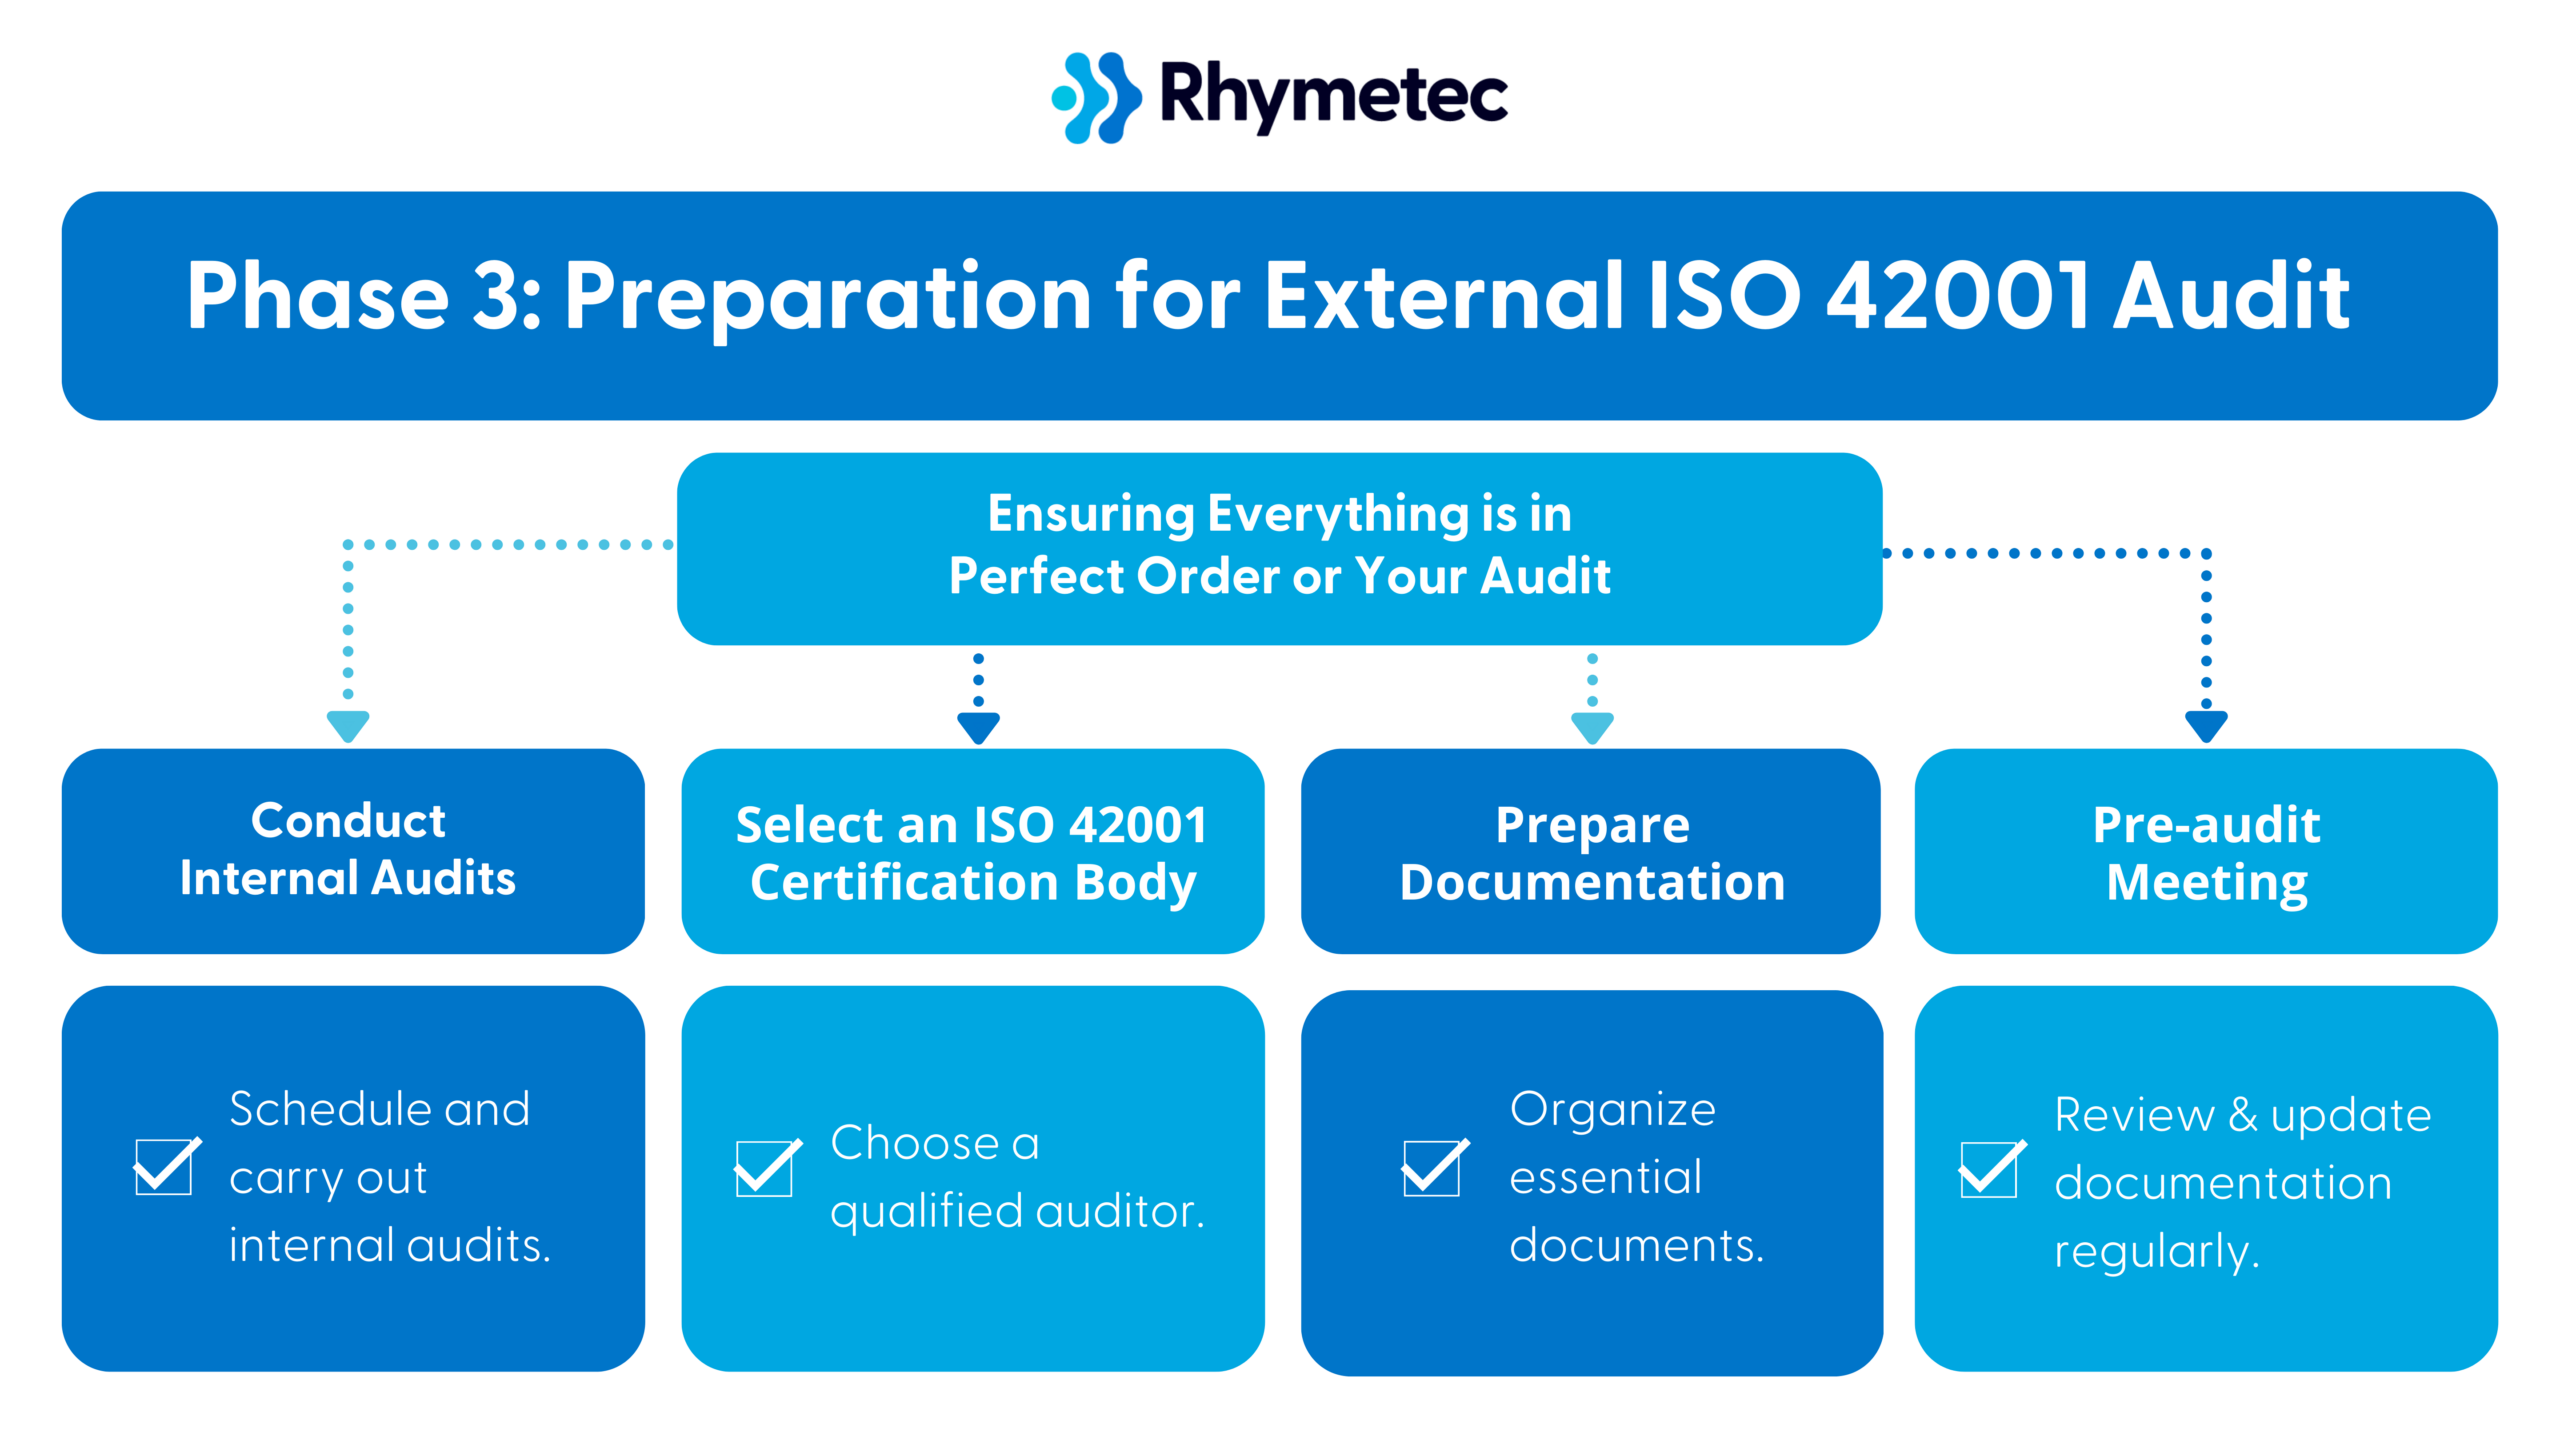
1. Conduct Internal Audits
Schedule and carry out internal audits.
ISO internal audits identify any gaps in compliance and provide recommendations for improvements before your external audit. It serves as a trial run, providing insights into potential audit challenges and giving you a chance to address any issues.
2. Select an ISO 42001 Certification Body
Choose a qualified auditor.
Select an auditing firm that has been certified to offer ISO certifications and has demonstrated experience in assessing AI management systems. Your certification body must be accredited to guarantee a legitimate audit and certification.
3. Prepare Documentation
Organize essential documents.
Gather documentation that demonstrates your compliance with ISO 42001. Documents are to include policies, procedures, control implementation records, and evidence of your plans for continuous improvement efforts.
Make things as easy as possible for your auditors! Documents should be in a format that is readily available and organized for easy reference during the audit.
Review and update documentation regularly.
Regularly review your AIMS documentation to make sure it accurately reflects current AI management practices and that all modifications are recorded. Keep this documentation accessible to all relevant personnel and the auditing team.
4. Pre-audit Meeting
Set up an initial audit meeting.
Arrange a meeting with the selected certification body to discuss the audit process. Use this as an opportunity to understand the audit scope, methodology, and specific focus areas. You should also align expectations and clarify the audit schedule.
Compile key audit questions.
Beforehand, prepare a list of questions and points needing clarification. Cover logistical details, specific compliance queries, and any concerns about the AIMS implementation.
Discuss audit scope.
You'll want to clarify the detailed scope of the audit and confirm that both parties have a mutual understanding of the audit boundaries. The scope must cover all relevant areas of your AIMS.
Phase 4: Obtaining your ISO 42001 Certification
This final phase is where all of your preparation pays off.
Engaging fully with auditors transforms this process from a compliance exercise to a powerful tool for improving your operations and reputation. Undergoing your audit isn't just a badge for your business to put on your website; it's a statement that you take AI risks seriously and are ahead of the curve in managing AI responsibly.
Lastly, continually improving after the audit shows you're not just "checking a box" to get through an audit. Ongoing improvements post-audit strengthen trust among clients and partners and support compliance maintenance.
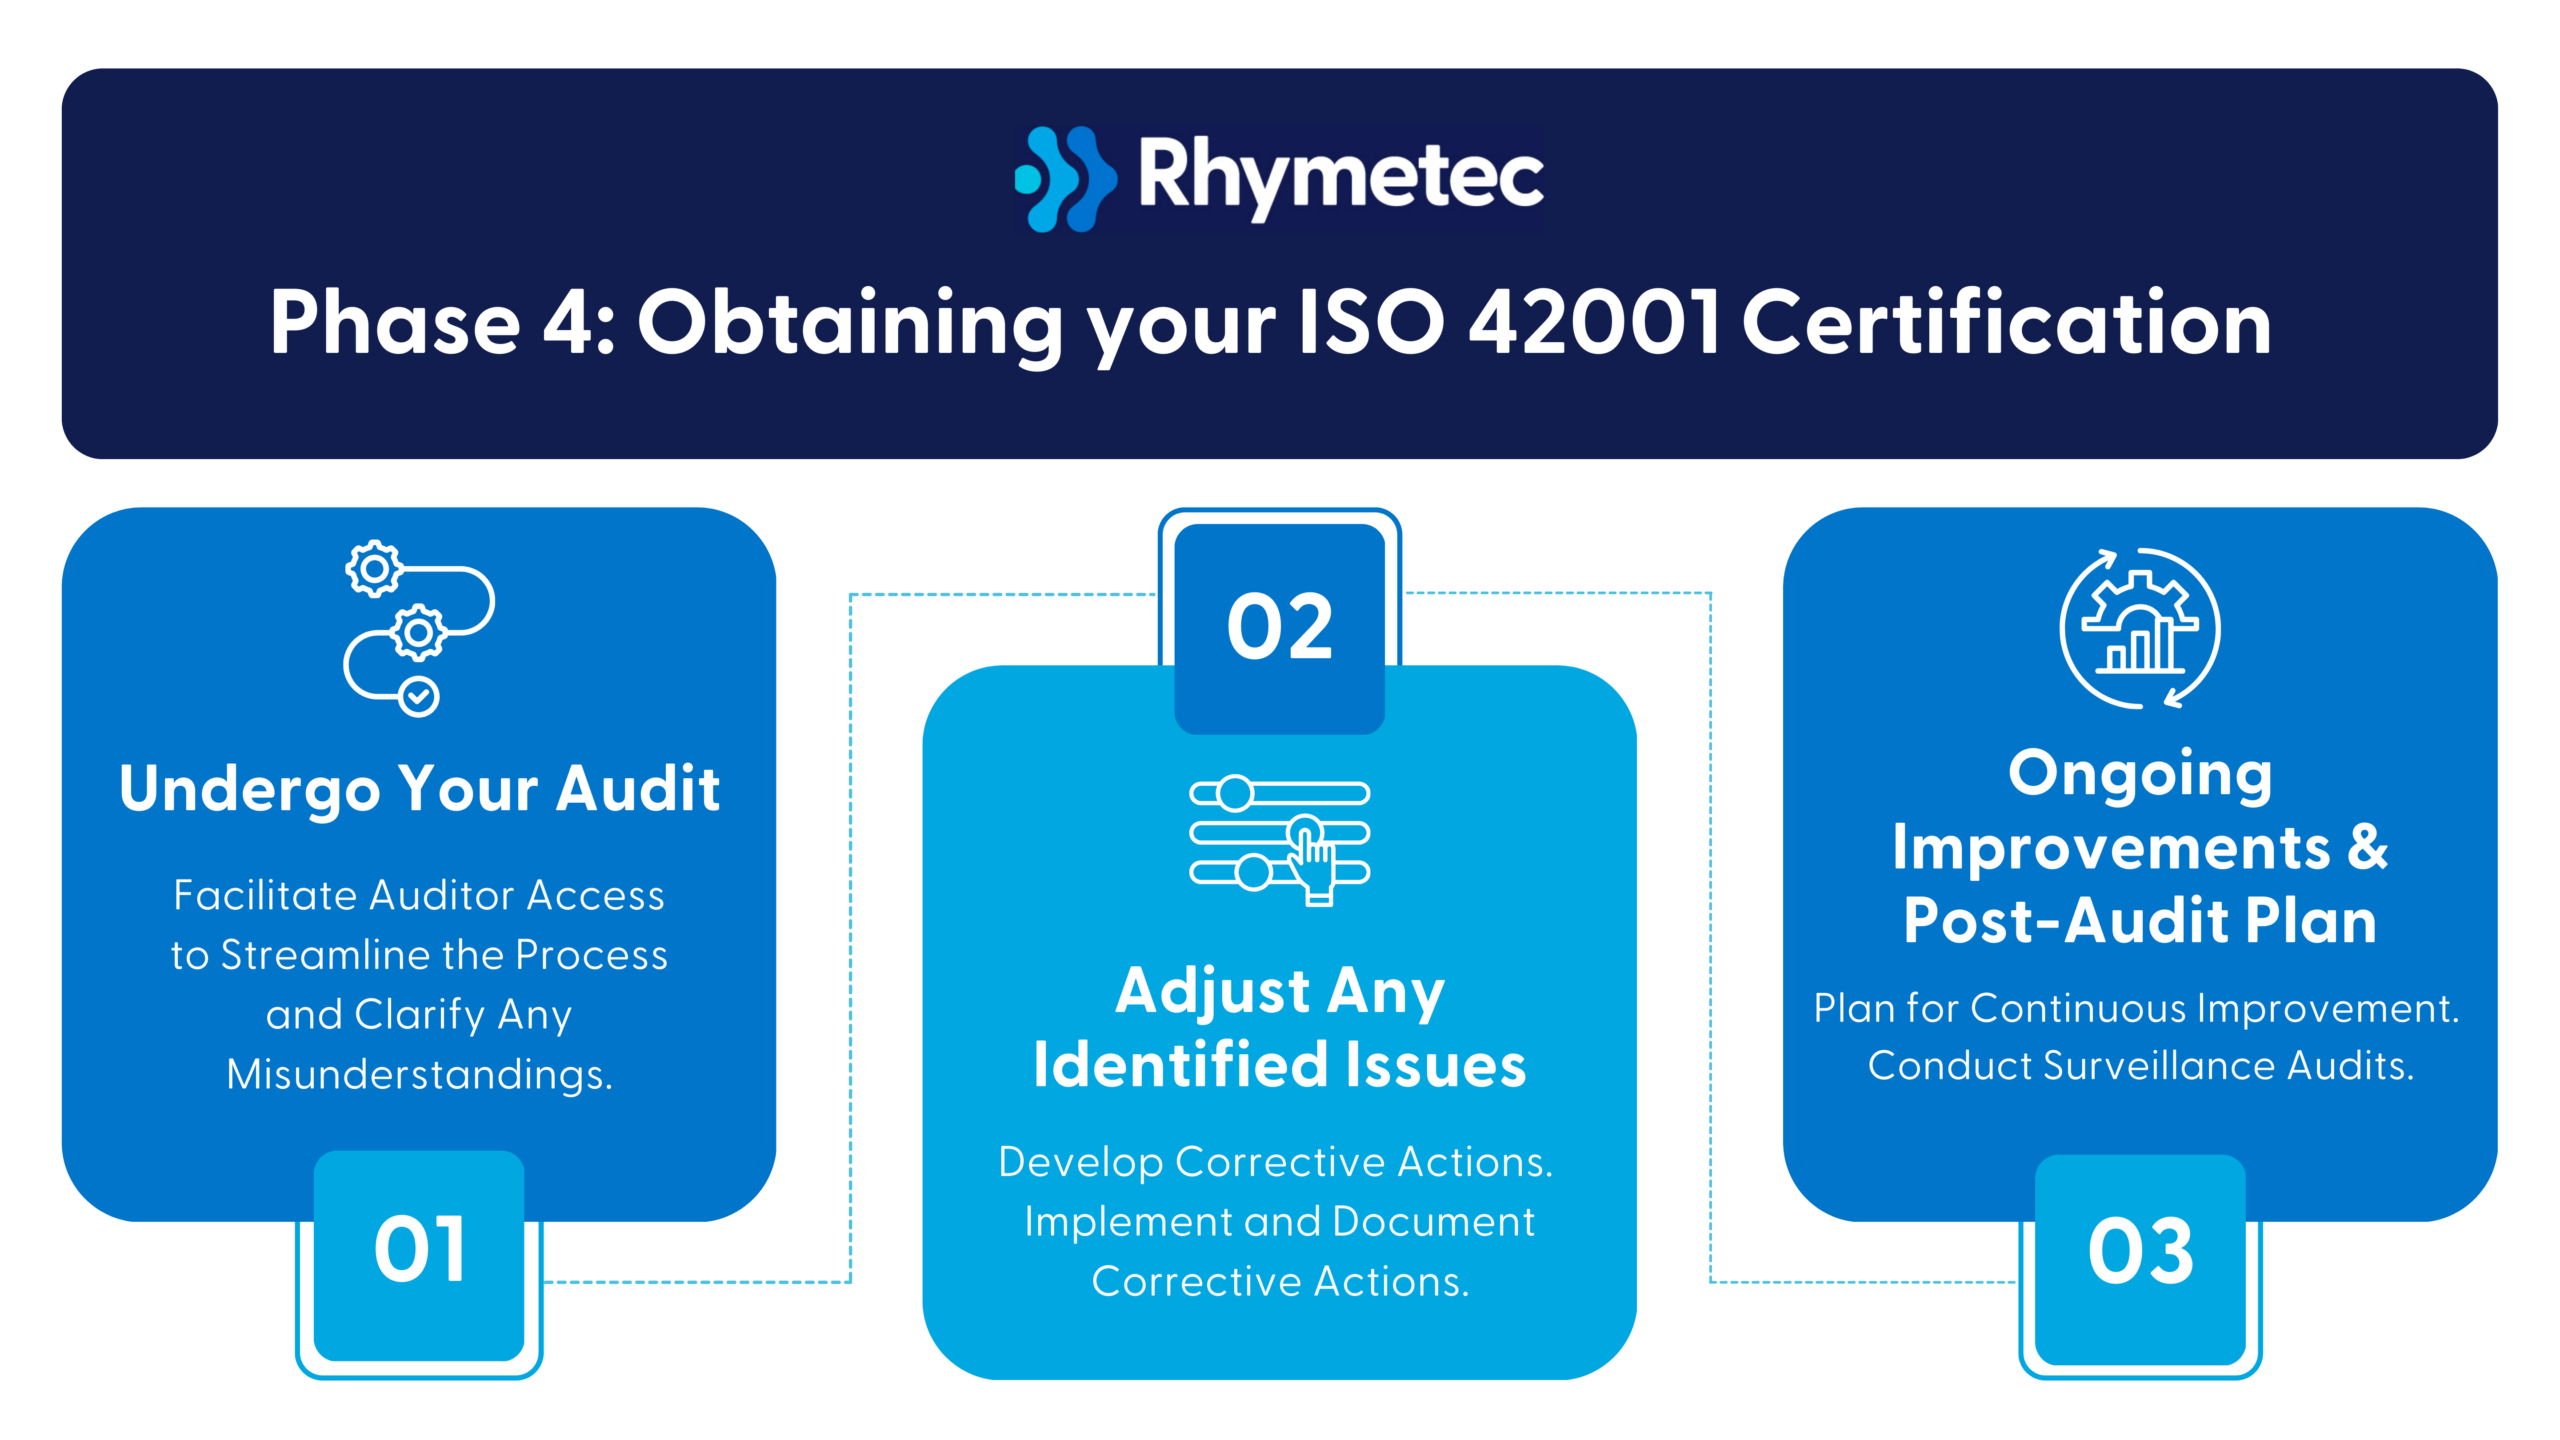
1. Undergo Your Audit
Facilitate Auditor Access.
Auditors need to have full access to all relevant sites, personnel, and documentation. Designate a team member to serve as a point of contact and participate in discussions with auditors to streamline the process and clarify any misunderstandings.
2. Address Any Identified Issues
Develop Corrective Actions.
Promptly create action plans for any non-compliance issues identified during the audit. Assign clear responsibilities and timelines for these actions.
Implement and Document Corrective Actions.
Execute the necessary corrective measures and document the processes. You will need this documentation during follow-up audits.
3. Ongoing Improvements & Post-Audit Plan
Plan for Continuous Improvement.
Develop a plan for continuous improvement based on audit findings.
Your post-audit plan should include updating training programs and communication with employees to address any changes. Schedule regular intervals to review the AIMS and identify opportunities to improve.
Conduct Surveillance Audits In Preparation to Re-certify Every 3 Years.
Lastly, keep in mind you will need future surveillance audits as part of your ongoing ISO 42001 process:
ISO 42001 requires recertification every 3 years to remain compliant. Surveillance audits are needed in between to ensure your organization is ready for the next official audit.
Immediate Benefits After Completing Your ISO 42001 Checklist
After you've completed all items in your ISO 42001 checklist and have your certification in hand, you will see a number of immediate benefits:
You will now be able to communicate, through verified third-party documentation, to your prospects and customers that your AI use follows the highest industry standards. You can use your certification to assuage any concerns your clients and prospects may have about AI. Being able to show them your documentation increases trust and can shorten your sales cycle. This is especially important given that there is growing concern over generative AI security risks.
Additionally, you will have peace of mind knowing that your risk is substantially reduced. The roadmap you now have for the strategic use of AI will serve as a business enabler as you continue to expand your AI offerings and break into new marketplaces.
For more information, check out our ISO 42001 Compliance FAQ for the most common questions our team at Rhymetec sees about ISO 42001 (Who Needs ISO 42001?, How Different Is ISO 42001 Vs. ISO 27001?, How Much Does ISO 42001 Certification Cost?, How Long Does ISO 42001 Certification Take?, and more), or contact our team today:
About Rhymetec
Our mission is to make cutting-edge cybersecurity available to SaaS companies and startups. We've worked with hundreds of companies to provide practical security solutions tailored to their needs, enabling them to be secure and compliant while balancing security with budget. We enable our clients to outsource the complexity of security and focus on what really matters – their business.
If your organization is interested in exploring compliance with AI standards, we now offer ISO/IEC 42001 certification readiness and maintenance services and are happy to answer any questions you may have on the ISO 42001 process.
Interested in reading more? Check out more content on our blog.
Artificial Intelligence (AI) is transforming multiple sectors, driving innovation and enhancing productivity and cybersecurity. The AI market is projected to rise from an estimated $86.9 billion in revenue in 2022 to $407 billion by 2027. This technology is reshaping industries and is expected to have a significant economic impact, with a projected 21% net increase in the US GDP by 2030. However, despite its advantages, AI also creates cybersecurity challenges in the hands of malicious actors. Businesses must navigate this complex issue to harness the benefits of AI, while safeguarding against its misuse.
Recognizing the Threat of Malicious AI
Malicious AI can cause sizable problems for cybersecurity crews. For example, its increased use in phishing attempts is a concern, as it mimics human interaction to craft targeted, convincing phishing emails. Additionally, AI can be used to identify security vulnerabilities that humans may sometimes miss and allow attackers to exploit these vulnerabilities. Many of these threats are currently still theoretical, but they are likely advancing faster than we realize.
Prioritizing Security in Product Design
In light of the growing threat of malicious AI, embedding cybersecurity principles into product design is critical. Incidents such as the Samsung data breach attributed to ChatGPT underscore the risks of sidelining security. As AI draws data from multiple sources, businesses must implement AI policies and tools like mobile device management and endpoint protection software to prevent misuse. Prioritizing security from the outset of product development is key to building user trust.
Achieving Collaboration Among Teams
While dedicated cybersecurity teams are common in enterprise companies, security remains a collective responsibility for all employees. A vigorous approach to security requires collaboration across departments to keep everyone aligned with best practices. Security awareness training is one of the best ways organizations can remind their employees about their responsibilities when it comes to cyber security risks. Paying attention to suspicious emails and protecting corporate credentials are some of the best practices employees may need training on. Dedicated product security managers, working with competent, collaborative teams can ensure companies continuously update their security measures and deploy AI to identify vulnerabilities effectively.
Guarding Against AI Exploitation
Generative AI tools like ChatGPT have changed how people work and improved productivity, but their ability to simulate human communication poses risks. While no AI-specific security regulations exist yet, initiatives like ISO's AI cybersecurity framework are in the works. Additionally, discussions are taking place about using AI to automate processes like network penetration tests, because it can identify vulnerabilities as well as human experts do. Due to AI’s “new” nature, many organizations are implementing internal AI policies to control how their employees and systems interact with AI. Some are even completely banning the use of generative AI tools to guard themselves against exploitation. These initiativesreflect the industry's commitment to secure AI use.
Streamlining Cybersecurity with AI Automation
Businesses are using automation more and more for cybersecurity. While tools like AI perform security tasks faster, no automation solution can guarantee 100% accuracy. Over-reliance on automation can lead to assumptions that might not fit every scenario. Regular audits and human oversight are essential to ensure the effectiveness of AI tools.
AI significantly speeds up certain tasks, such as responding to lengthy security questionnaires or RFQs. These can often be long, with some containing over 1000 questions. Businesses can answer these much faster with AI, saving both time and human resources.
In addition, incorporating AI into intrusion detection can enable systems to go beyond simple rule-checking to identify suspicious user behavior and network activity. For example, if a high-privilege user behaves unusually, AI can promptly sound the alert.
Navigating Compliance and Ethics in AI-Driven Cybersecurity
As AI-driven security measures become more common, companies must follow existing regulations like GDPR and CCPA. These regulations are designed to protect user data and privacy, and any AI system, including security protocols, must adhere to them. AI can benefit cybersecurity only if it does not compromise user privacy or data protection standards. Compliance with regulations safeguards users and protects organizations from potential legal fallout.
Ethical considerations are also paramount for companies implementing AI in cybersecurity. While enforcing information security policies is advisable, it's equally important to ensure employees understand and acknowledge them. This understanding gives organizations a level of assurance. If employees act against the policies, companies have a foundation for actions ranging from disciplinary measures to potential termination.
Anticipating an AI-Driven Cybersecurity Future
A lot is happening that is very exciting. Integrating AI with technologies like IoT and blockchain presents both opportunities and risks. Quantum computing's potential, though still in the early stages, promises computational power that can both bolster AI's capabilities and pose threats if misused. The tech world is abuzz with the potential of deep learning AI and LLMs, especially for automation.
AI's future role in cybersecurity is undeniable, but it offers promise and peril for companies. Enterprise organizations must find a way forward, benefitting from its strengths while staying vigilant against its potential pitfalls.
About The Author: Metin Kortak has been working as the Chief Information Security Officer at Rhymetec since 2017. He started out his career working in IT Security and gained extensive knowledge on compliance and data privacy frameworks such as: SOC; ISO 27001; PCI; FEDRAMP; NIST 800-53; GDPR; CCPA; HITRUST and HIPAA.
Metin joined Rhymetec to build the Data Privacy and Compliance as a service offerings and under his leadership, the service offerings have grown to more than 200 customers and is now a leading SaaS security service provider in the industry.
You can read the original article posted in Cyber Defense Magazine by Rhymetec CISO, Metin Kortak.
About Rhymetec
Our mission is to make cutting-edge cybersecurity available to SaaS companies and startups. We’ve worked with hundreds of companies to provide practical security solutions tailored to their needs, enabling them to be secure and compliant while balancing security with budget. We enable our clients to outsource the complexity of security and focus on what really matters – their business. Contact us today to get started.
Interested in reading more? Check out more content on our blog: